Sixteen regulatory-anchored modules with the expertise built in — step-by-step guidance on every screen, 1,000+ ready-made templates, and Otto, your AI compliance analyst, one question away. Bundled into three simple plans so you pick the one that fits your firm. For FCA-regulated firms that need supervisory-grade evidence — fast.
14-day free trial · Take the tour
Every module maps to its FCA sourcebook, comes pre-loaded with expert templates and is wired into Otto for live MI and board-ready reports. Pick a module — the live screen first, the full detail beneath it. Click any screenshot to enlarge: this is the live product, not a mock-up.
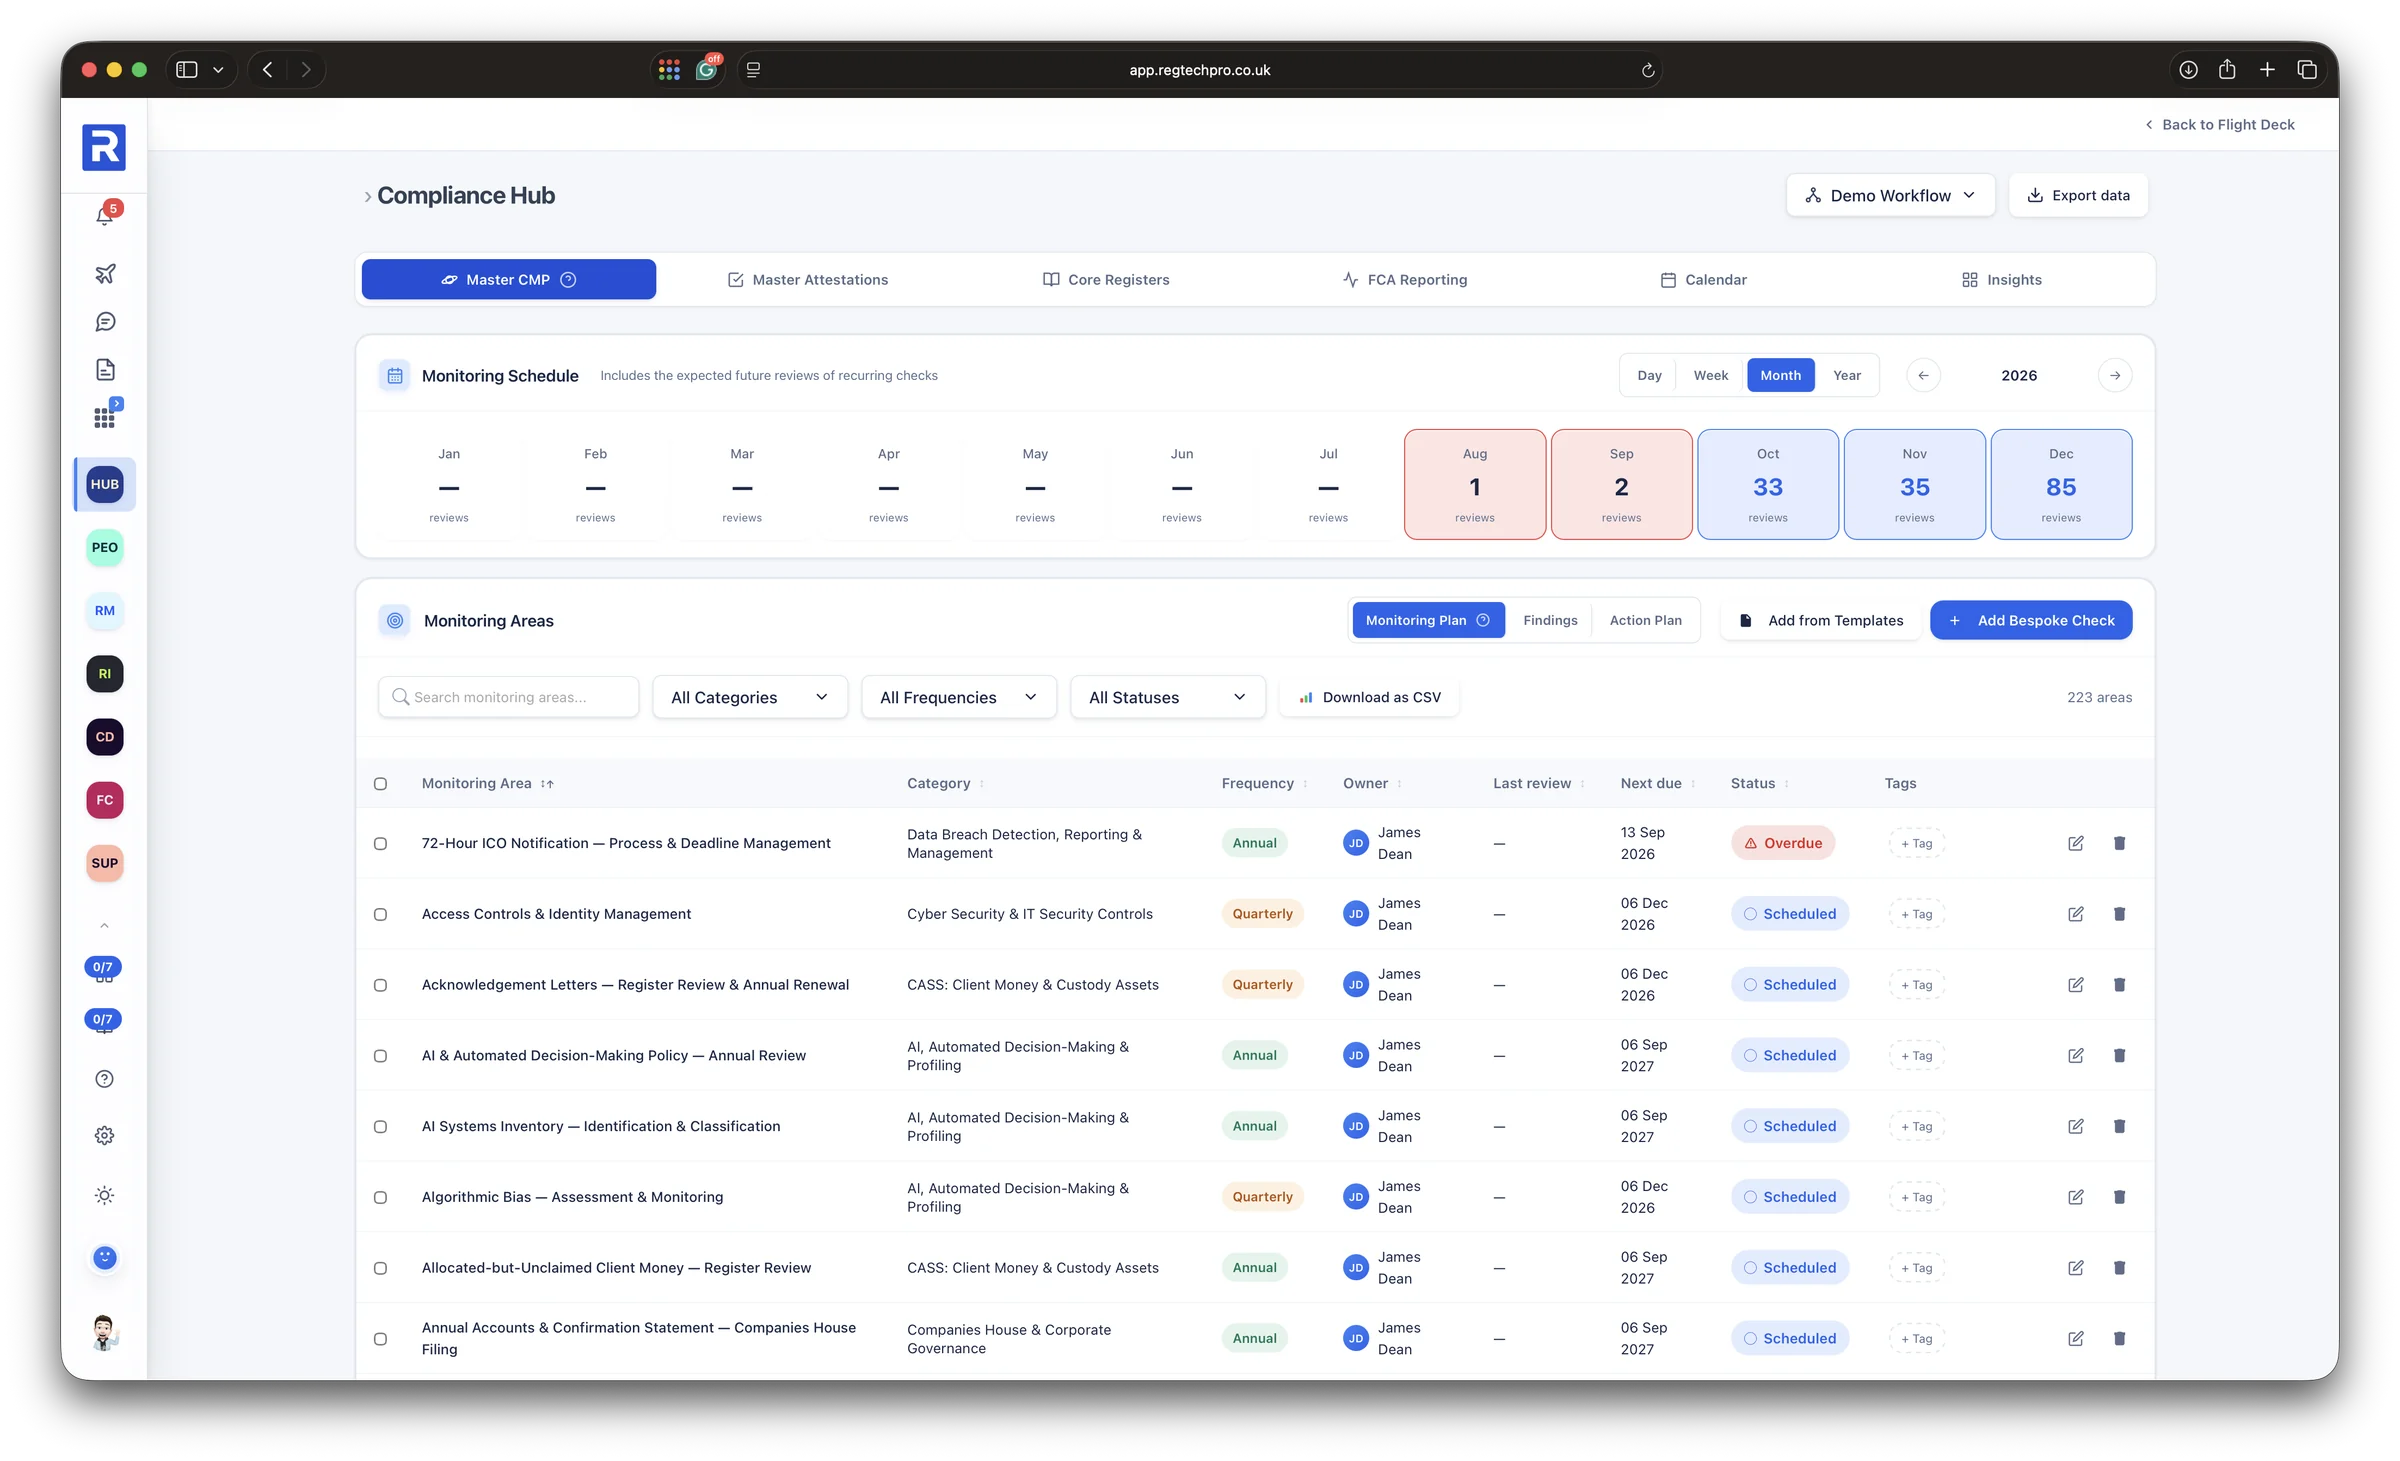
Your whole compliance monitoring programme in one place
The Compliance Hub runs the firm's entire compliance monitoring programme from one surface: 1,139 expert-built templates across 72 categories spanning seven regulators, plus a unified register for attestations, breaches, complaints, conflicts and custom forms, and every rule a check cites opens its current wording from the FCA Handbook. Handbook attestations walk eight sourcebooks chapter by chapter, MCOB and CONC included. A dual-mode calendar sets the firm's own tasks alongside 27 pre-loaded FCA regulatory events, and the Reports module builds a 12-section Compliance Monitoring Report from the plan's live data, with Otto writing the commentary. It is where the Compliance Officer runs the monitoring plan day to day.
Who it’s forCompliance Officers and SMF16 holders running a SYSC 6.1 monitoring programme, and consultants switching between several client firms from one login.
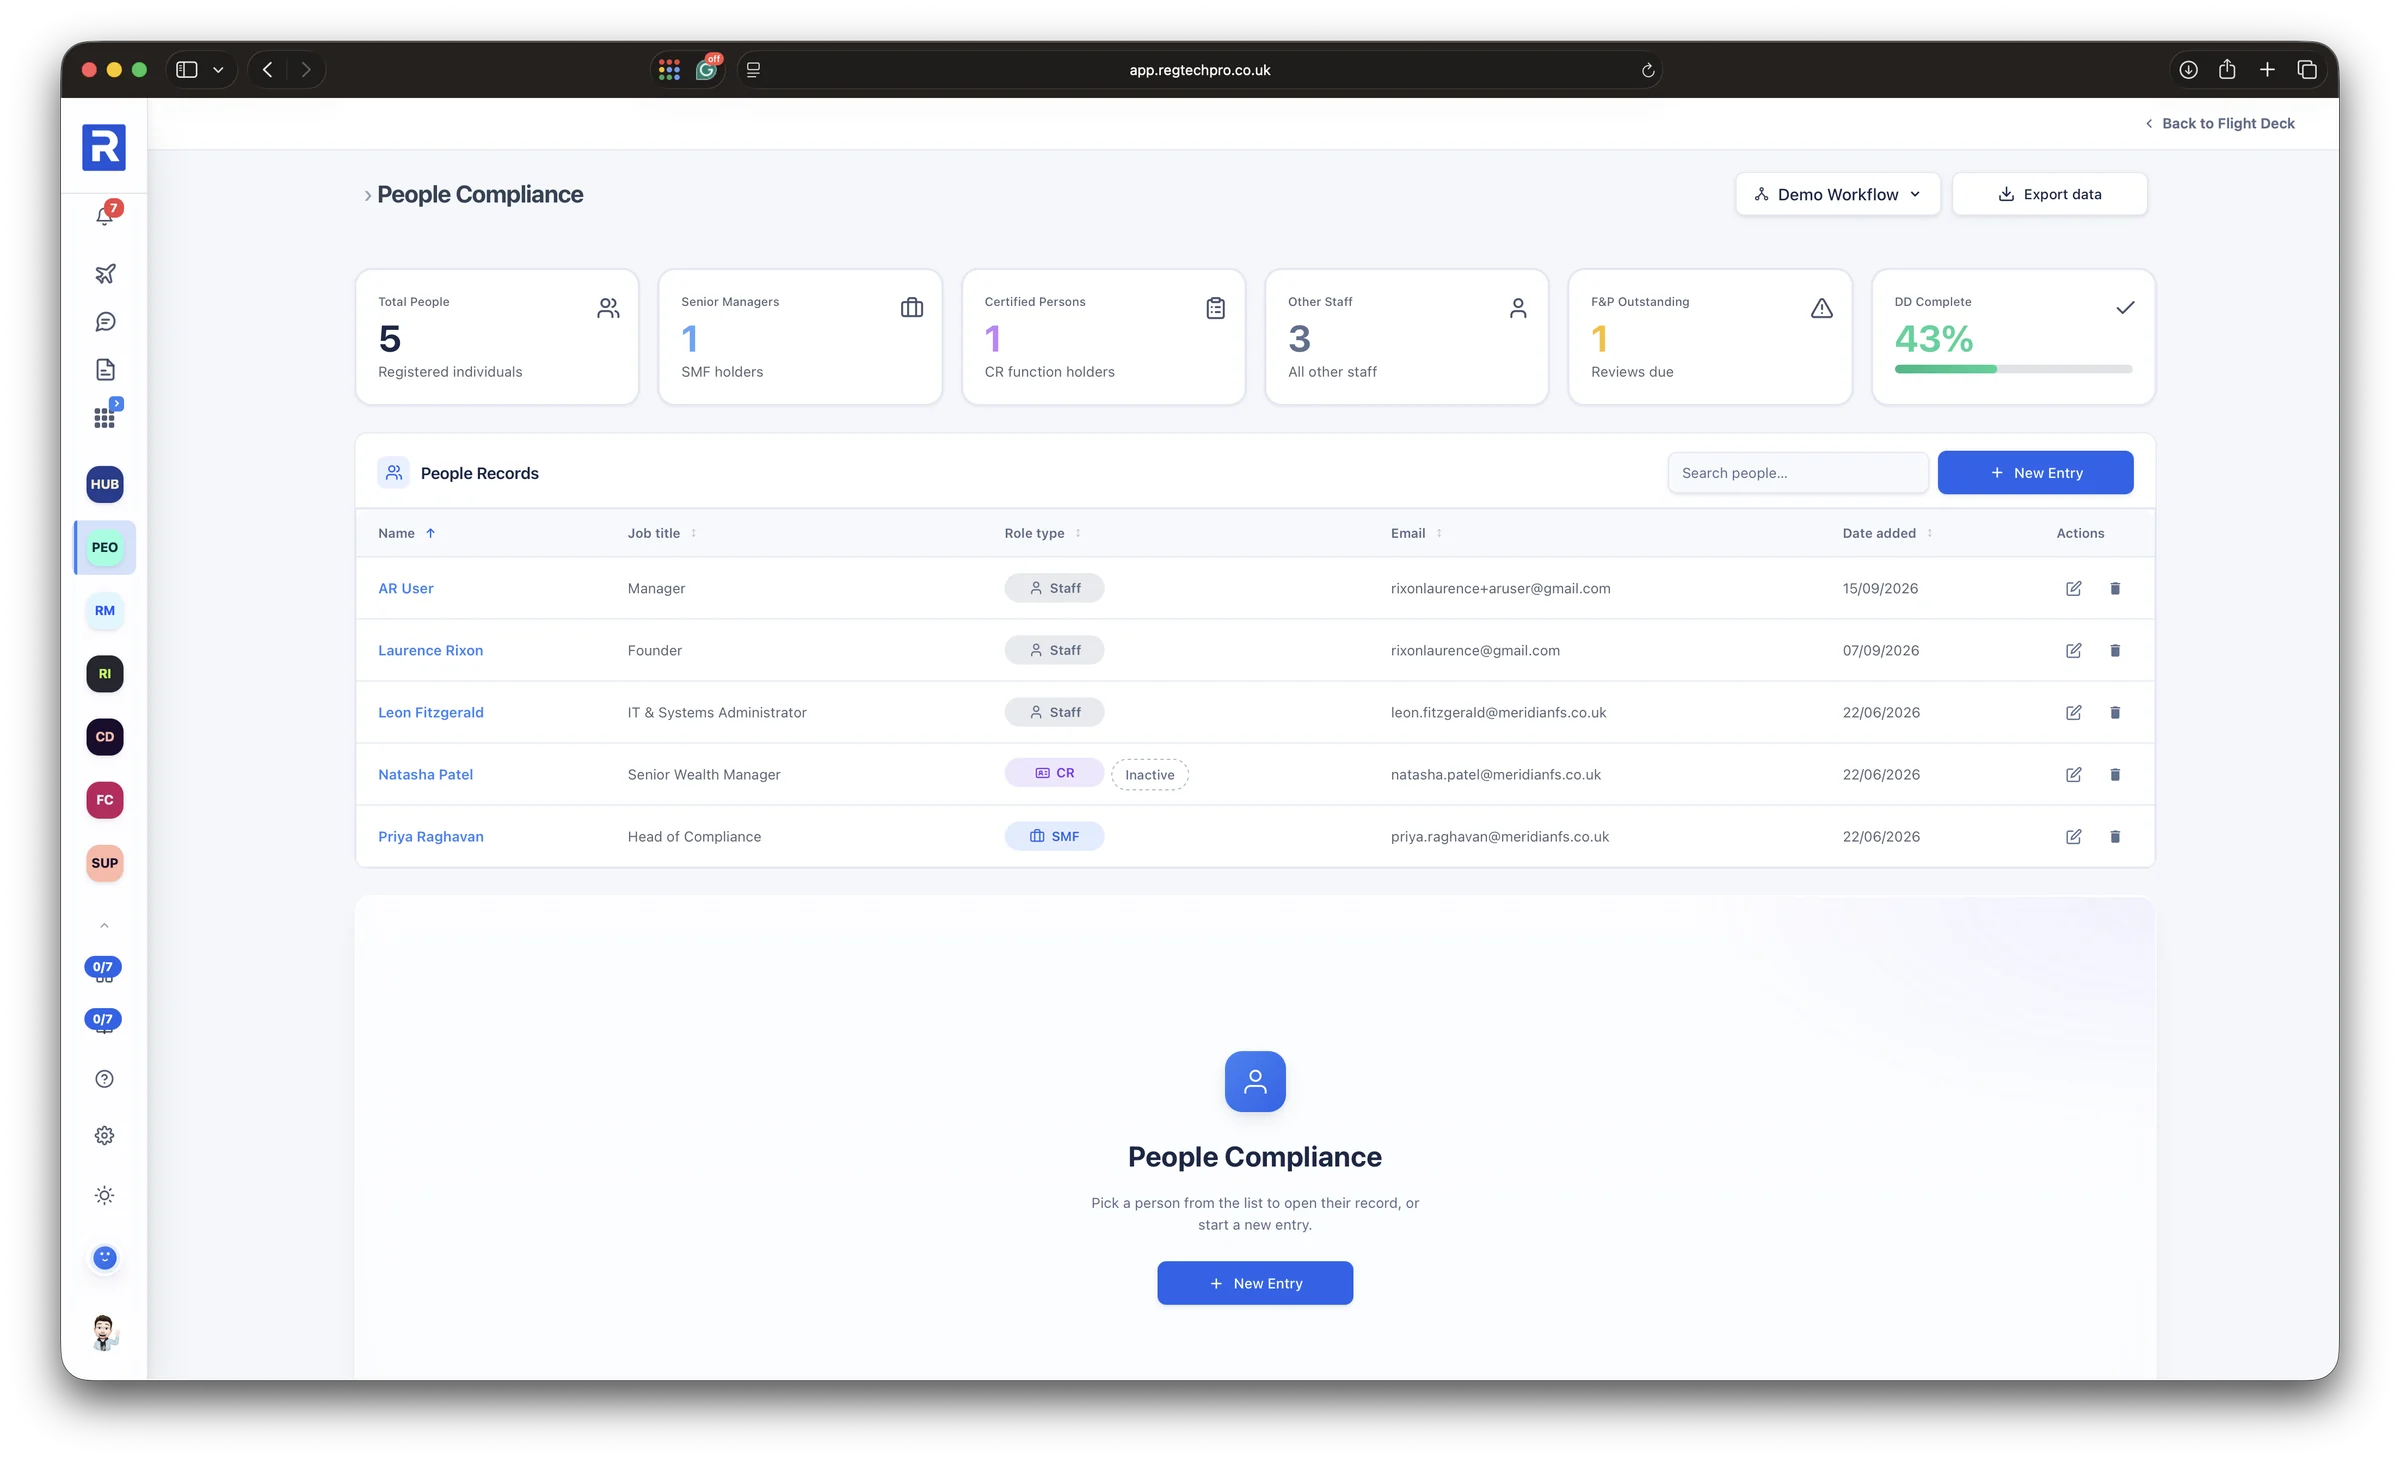
Every regulated individual, evidenced and certified
The SM&CR, APER and IDD operating system: a register of regulated individuals where each record opens a regime-aware editor covering the SMF Statement of Responsibilities, the FCA Form A Section 5 fit-and-proper assessment, annual certification, due diligence and CPD. It models who does the regulated work, and applies to every authorised firm — SM&CR has had no proportionality exemption since December 2019.
Who it’s forThe SMF16, Head of Compliance or HR-compliance lead at any FCA-authorised firm — universal, since every firm has at least one Senior Manager and certified staff.
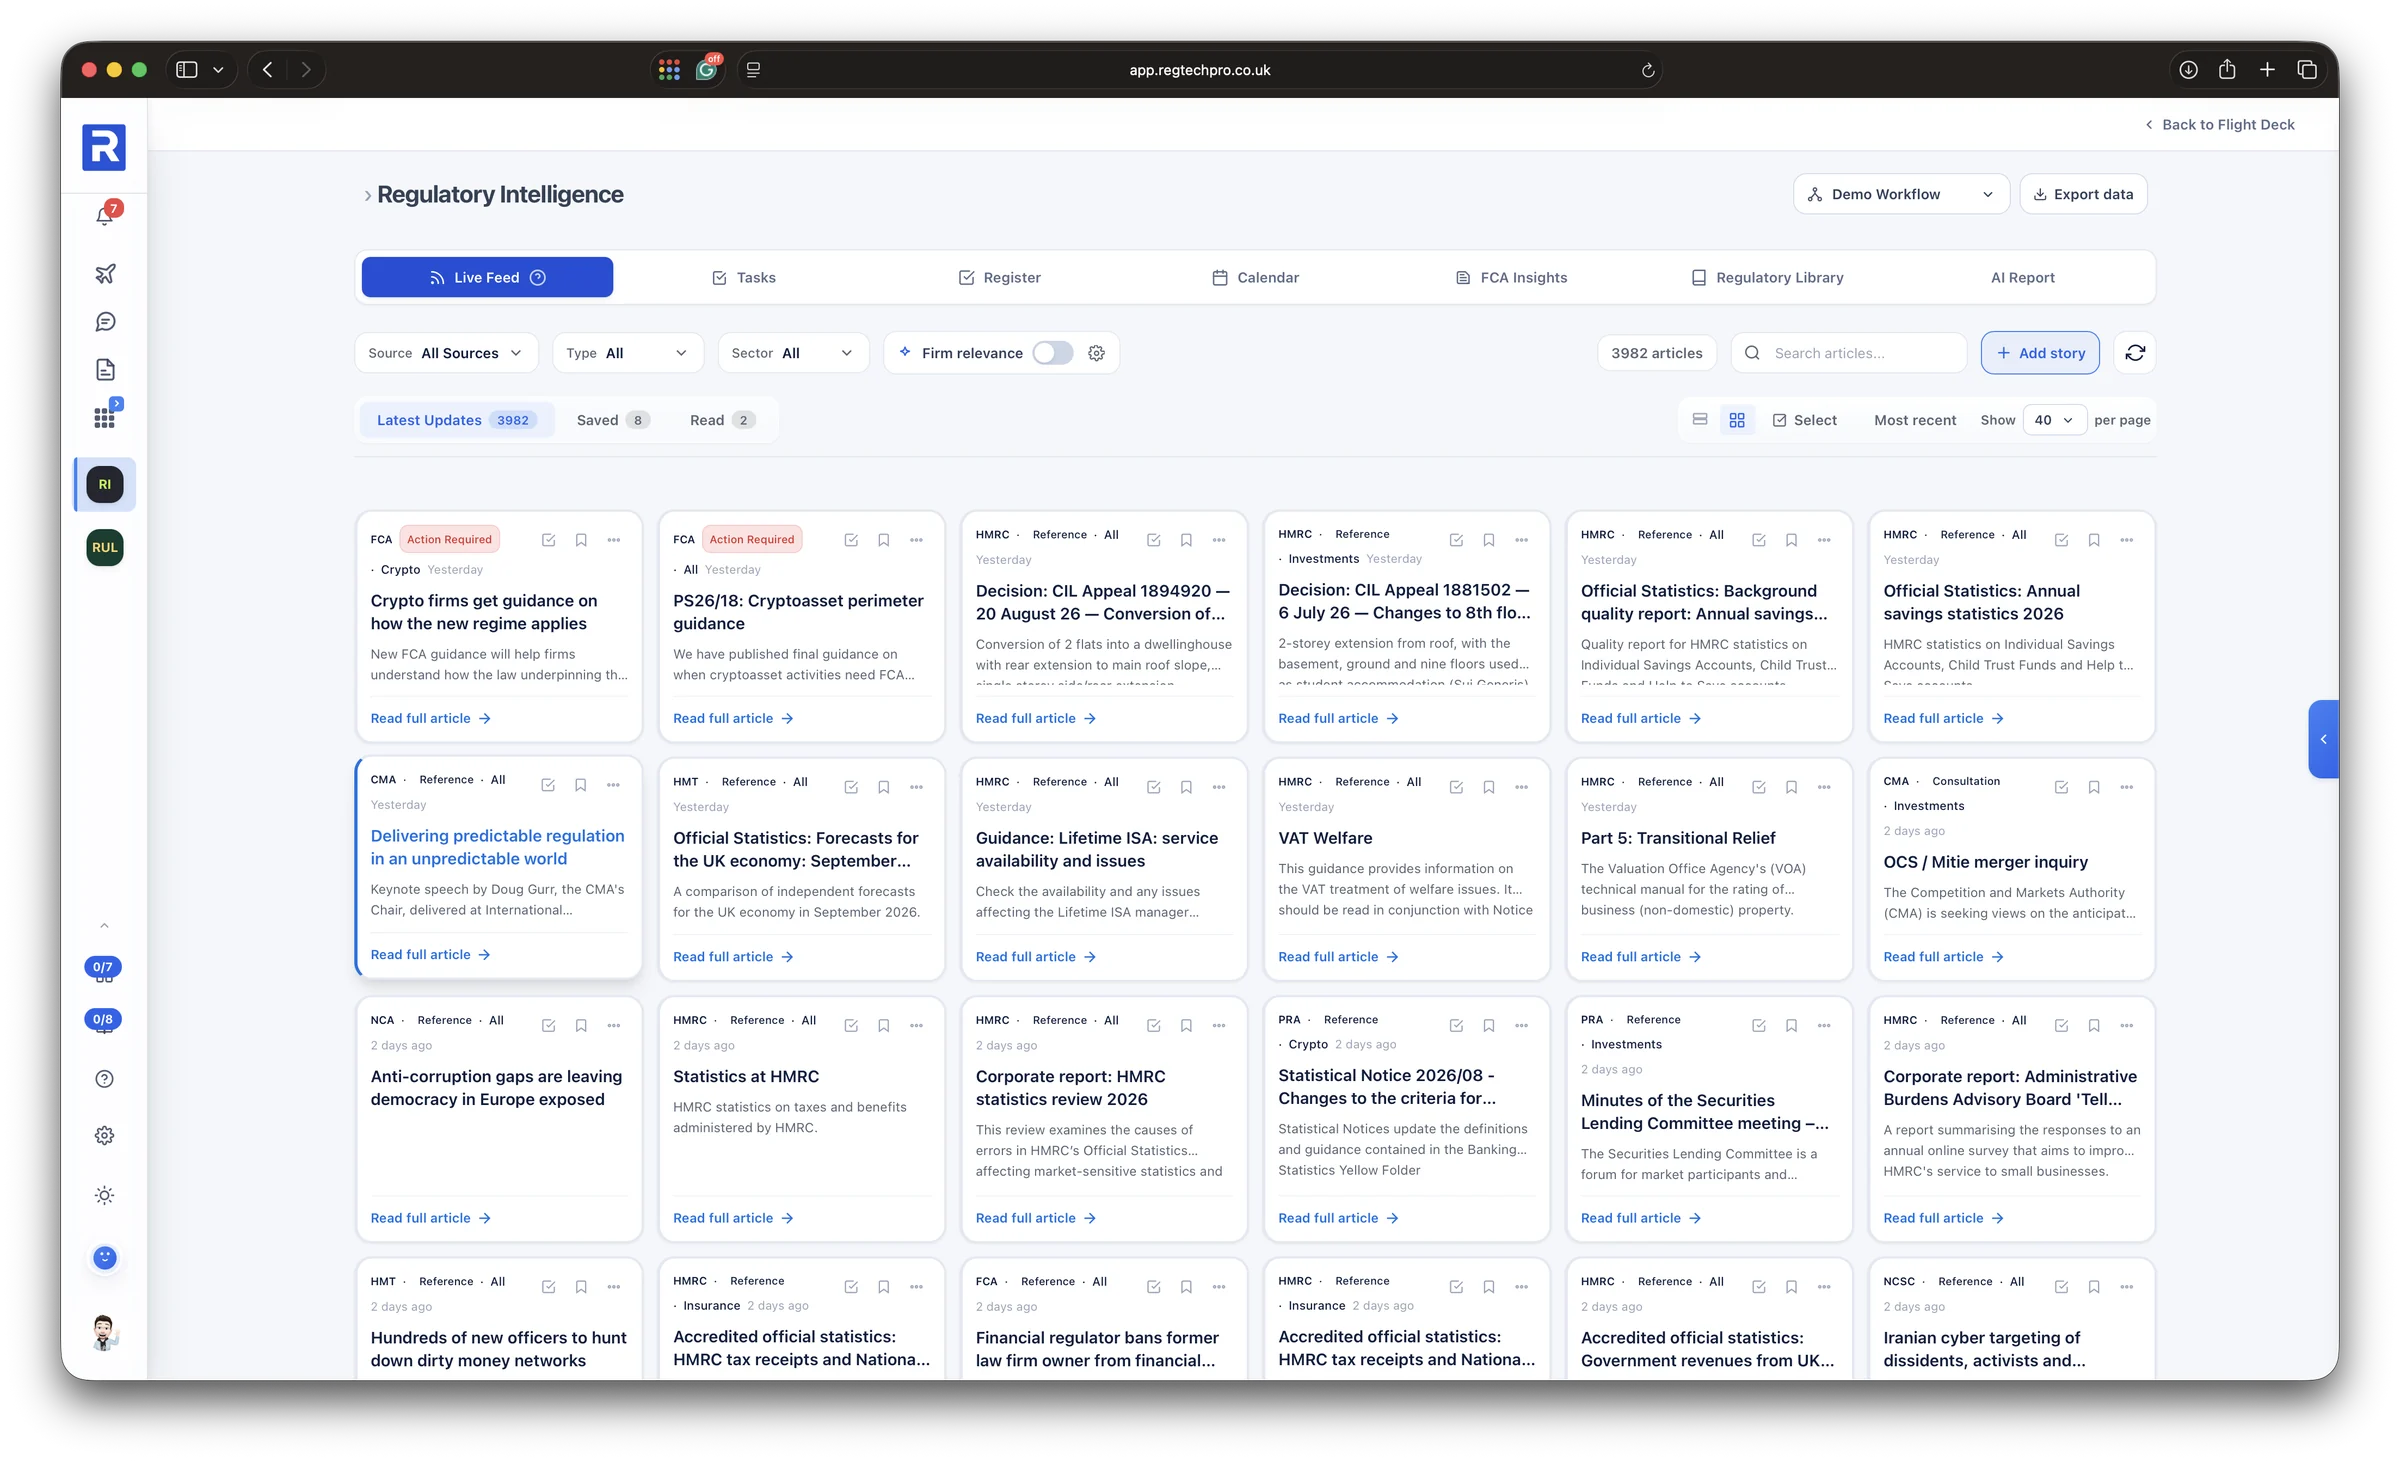
Thirteen UK regulators, filtered to your firm
Regulatory Intelligence unifies 13 UK regulators — FCA, PRA, ICO, OFSI and nine more — into a single feed refreshed hourly, holding around 2,600 live articles pre-classified by source, type and sector. Otto's firm-relevance filter narrows the feed to what affects your permissions and products, you assess each item in a regulatory change register with a full audit trail, and Otto drafts a board-ready report exported to Word or PDF.
Who it’s forFor UK FCA-regulated SME firms — compliance officers, MLROs and Heads of Compliance who need to track multiple regulators and evidence regulatory awareness.
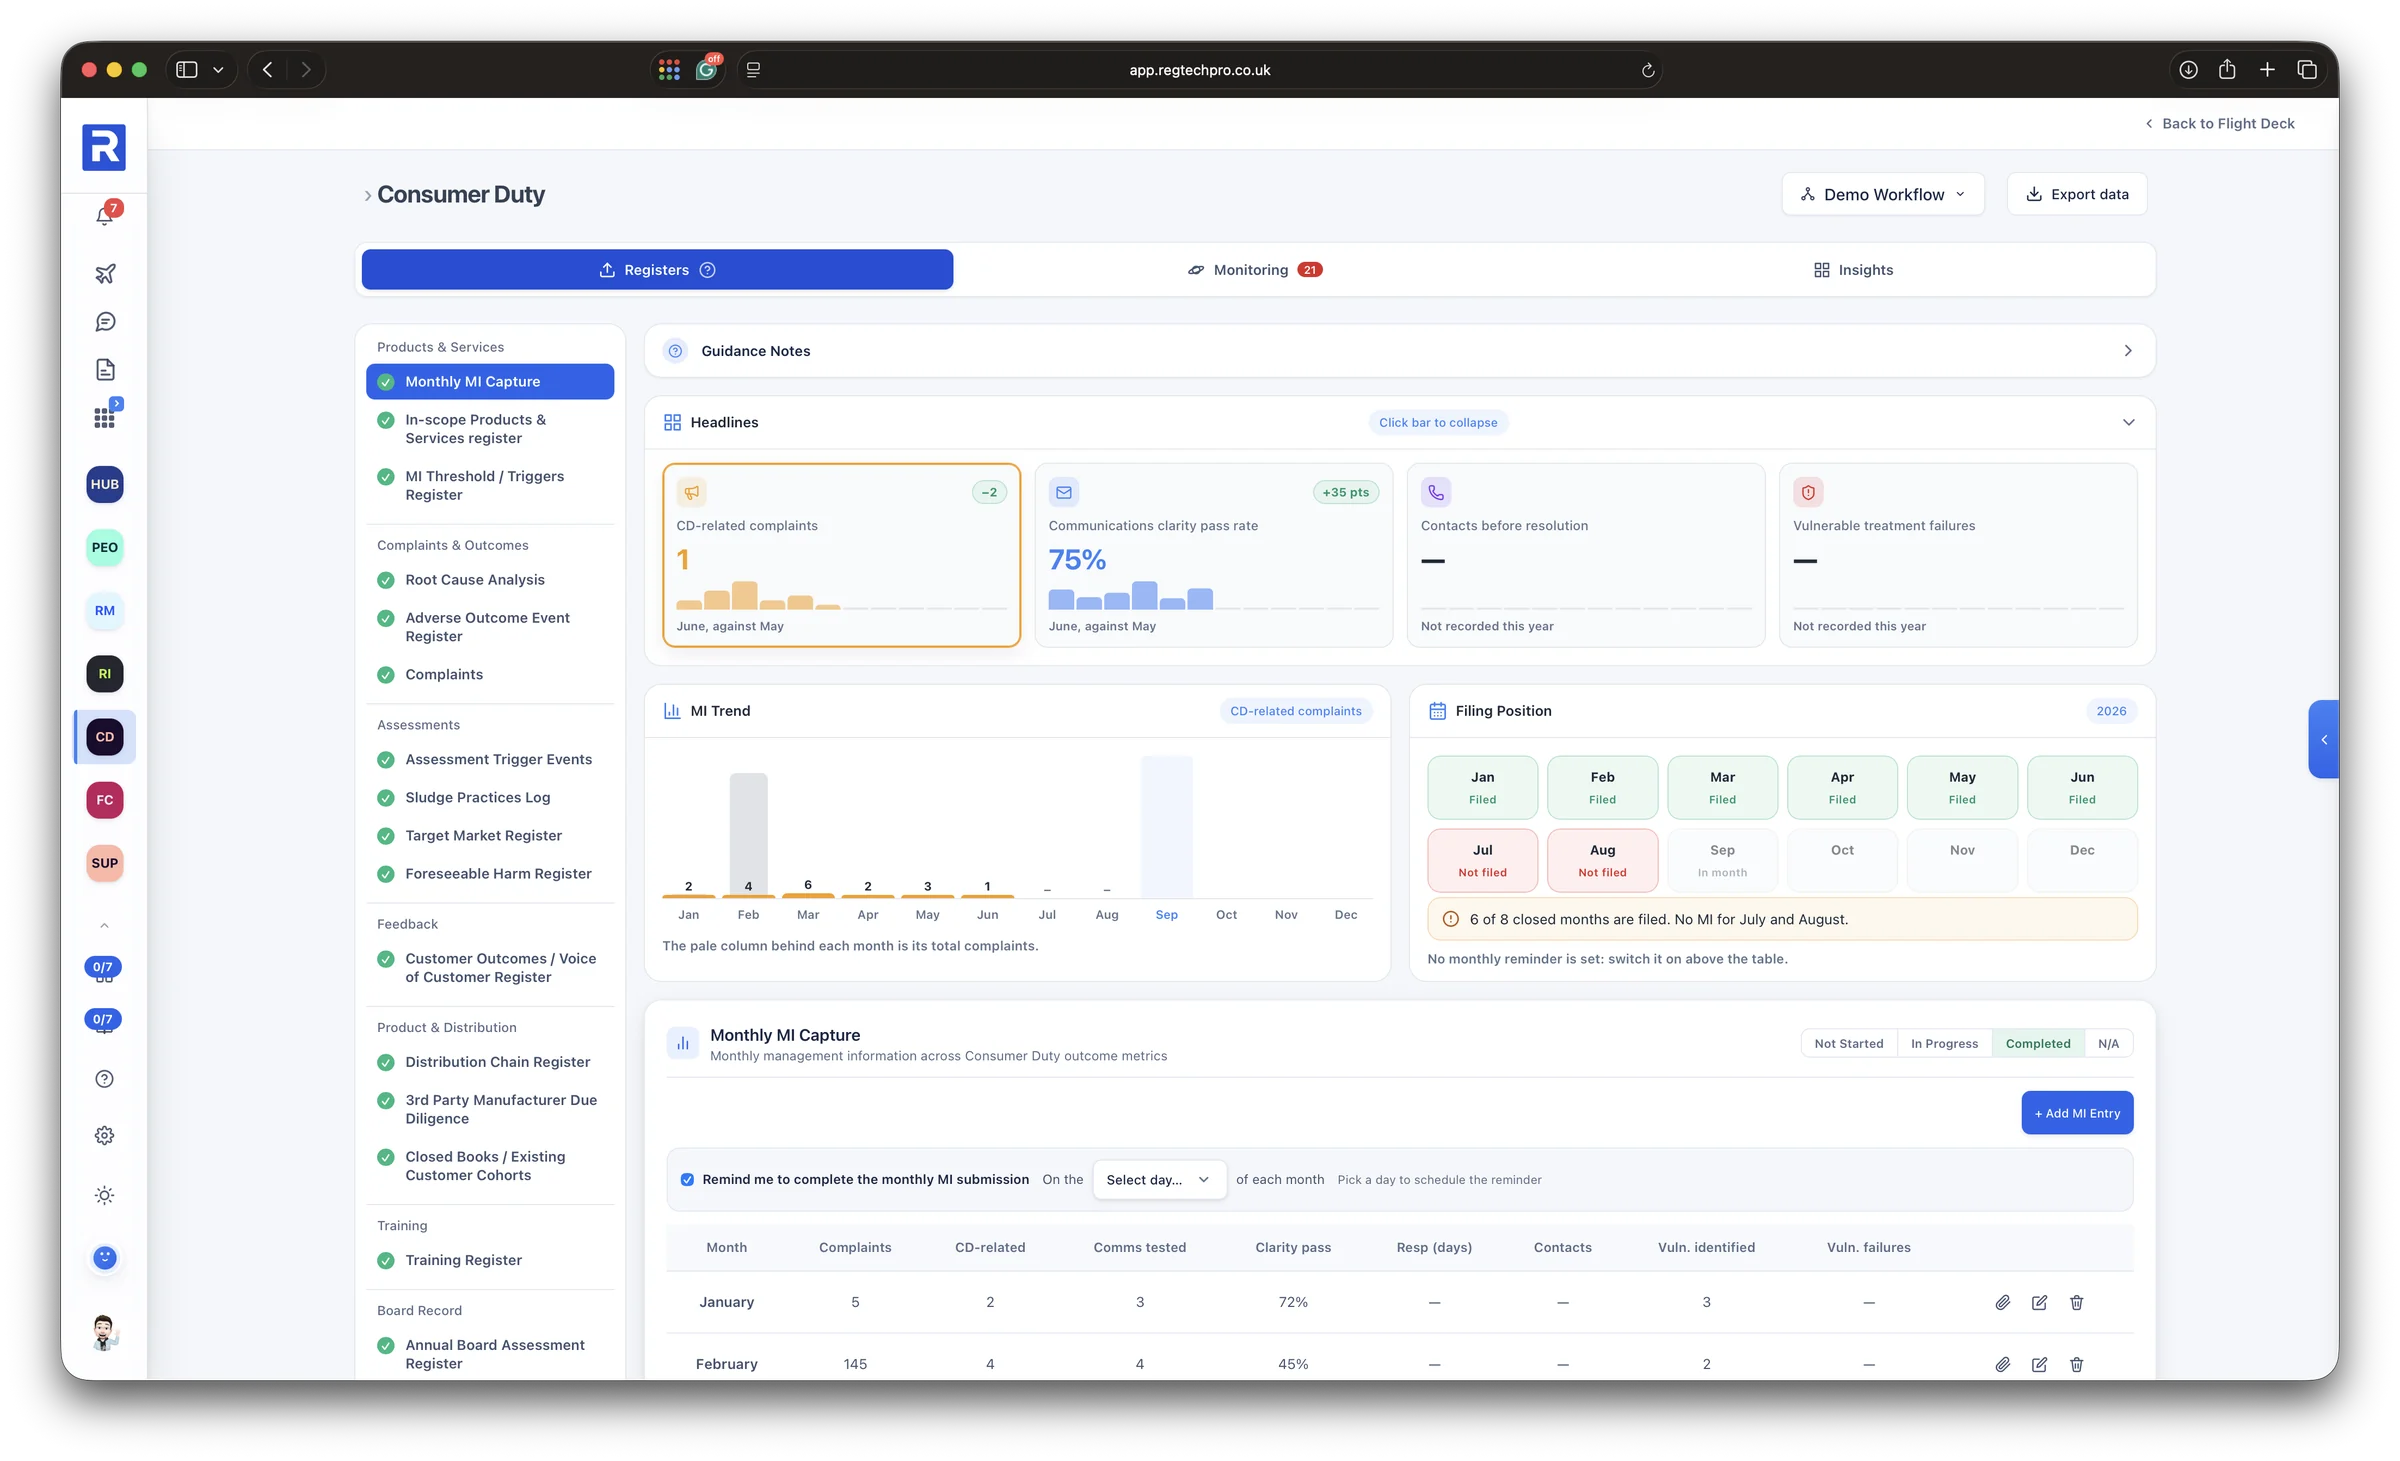
You attest, Otto drafts, your board signs
A complete operating layer for FCA Consumer Duty covering all four outcomes, the three cross-cutting rules and vulnerable-customer obligations. Humans attest on one firm attestation and a product review per product, and the Reports module builds the 13-section Annual Board Report from that live record, with Otto writing the commentary — the split of human input and sign-off the FCA expects to see. Every assertion in the report traces back to a named attestation, a register entry or a logged event.
Who it’s forThe roughly 80% of FCA-regulated firms with retail customers — retail banks, IFAs, wealth managers, consumer credit firms, insurance intermediaries and mortgage brokers subject to PRIN 2A.9.
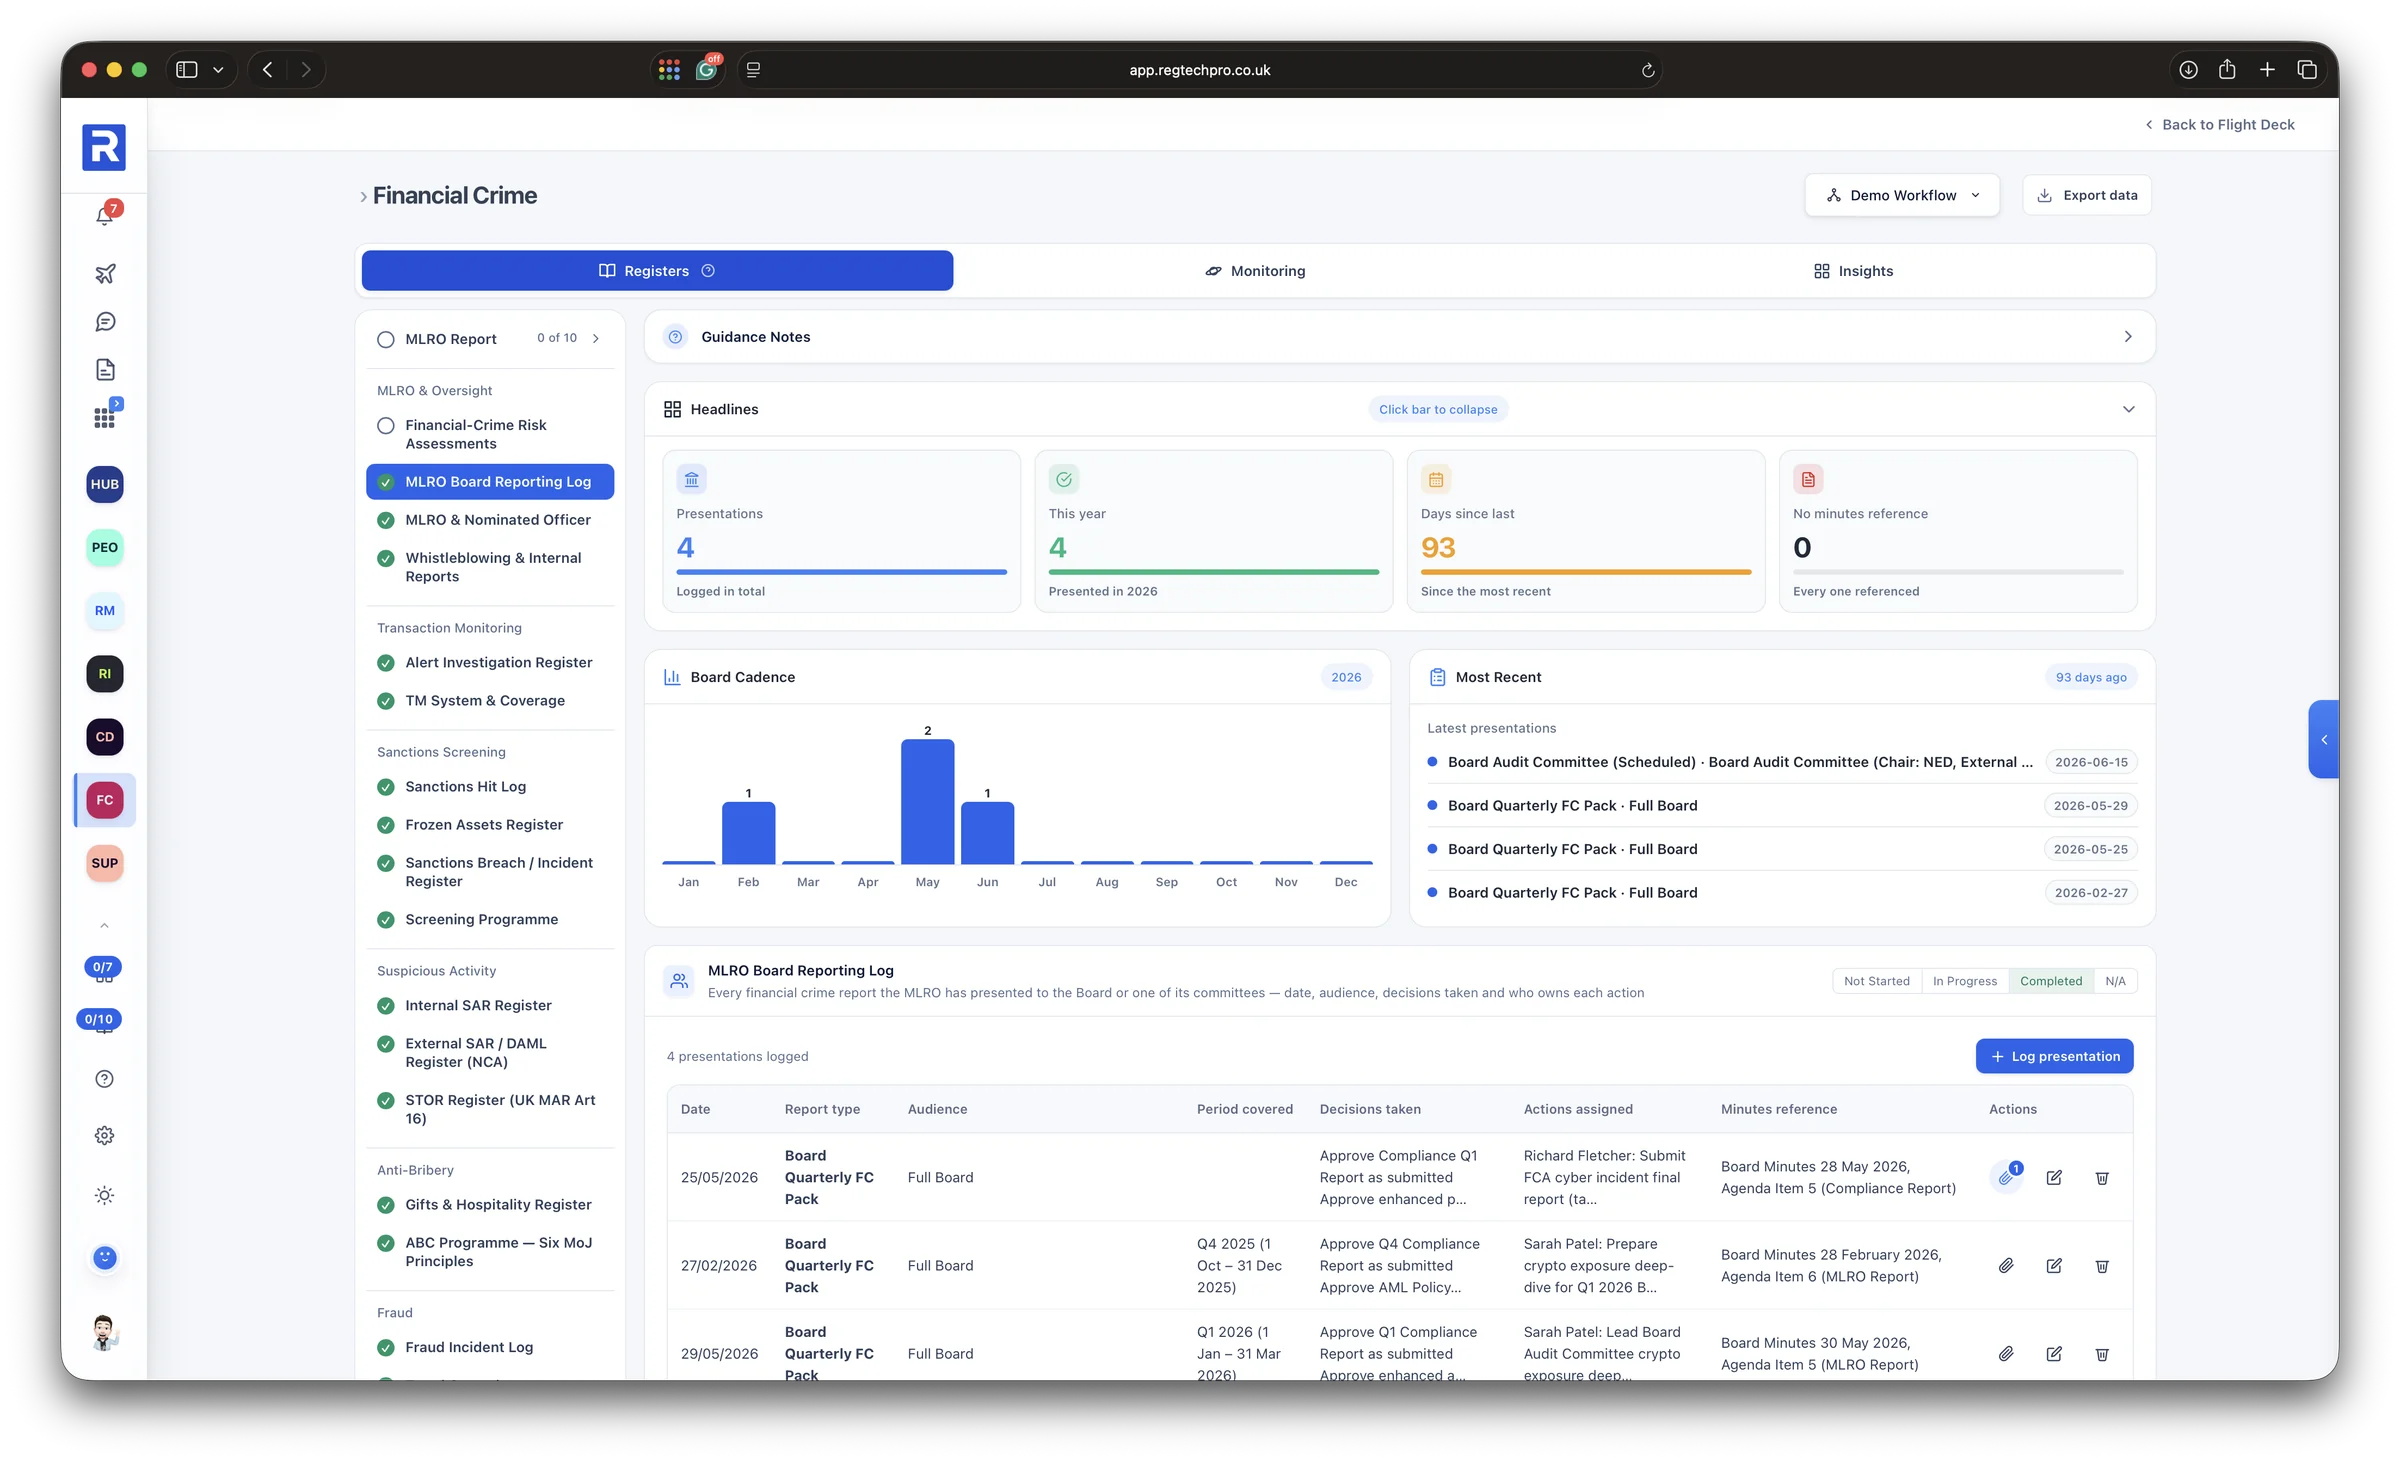
The MLRO's financial-crime operating system
Financial Crime is a complete MLRO workflow that turns every FCA and statutory financial-crime obligation into structured data capture, registers, evidence and Otto-drafted regulatory reports. It spans eight regimes — AML, transaction monitoring, sanctions, anti-bribery, SAR/STOR, market abuse, tax evasion and fraud — with customer due diligence in the Due Diligence module, and one Financial Crime score across 12 pillars. It replaces the MLRO's spreadsheet stack and much of an outsourced AML consultant.
Who it’s forFor the MLRO or Nominated Officer at an FCA-regulated firm running and evidencing a full financial-crime programme.
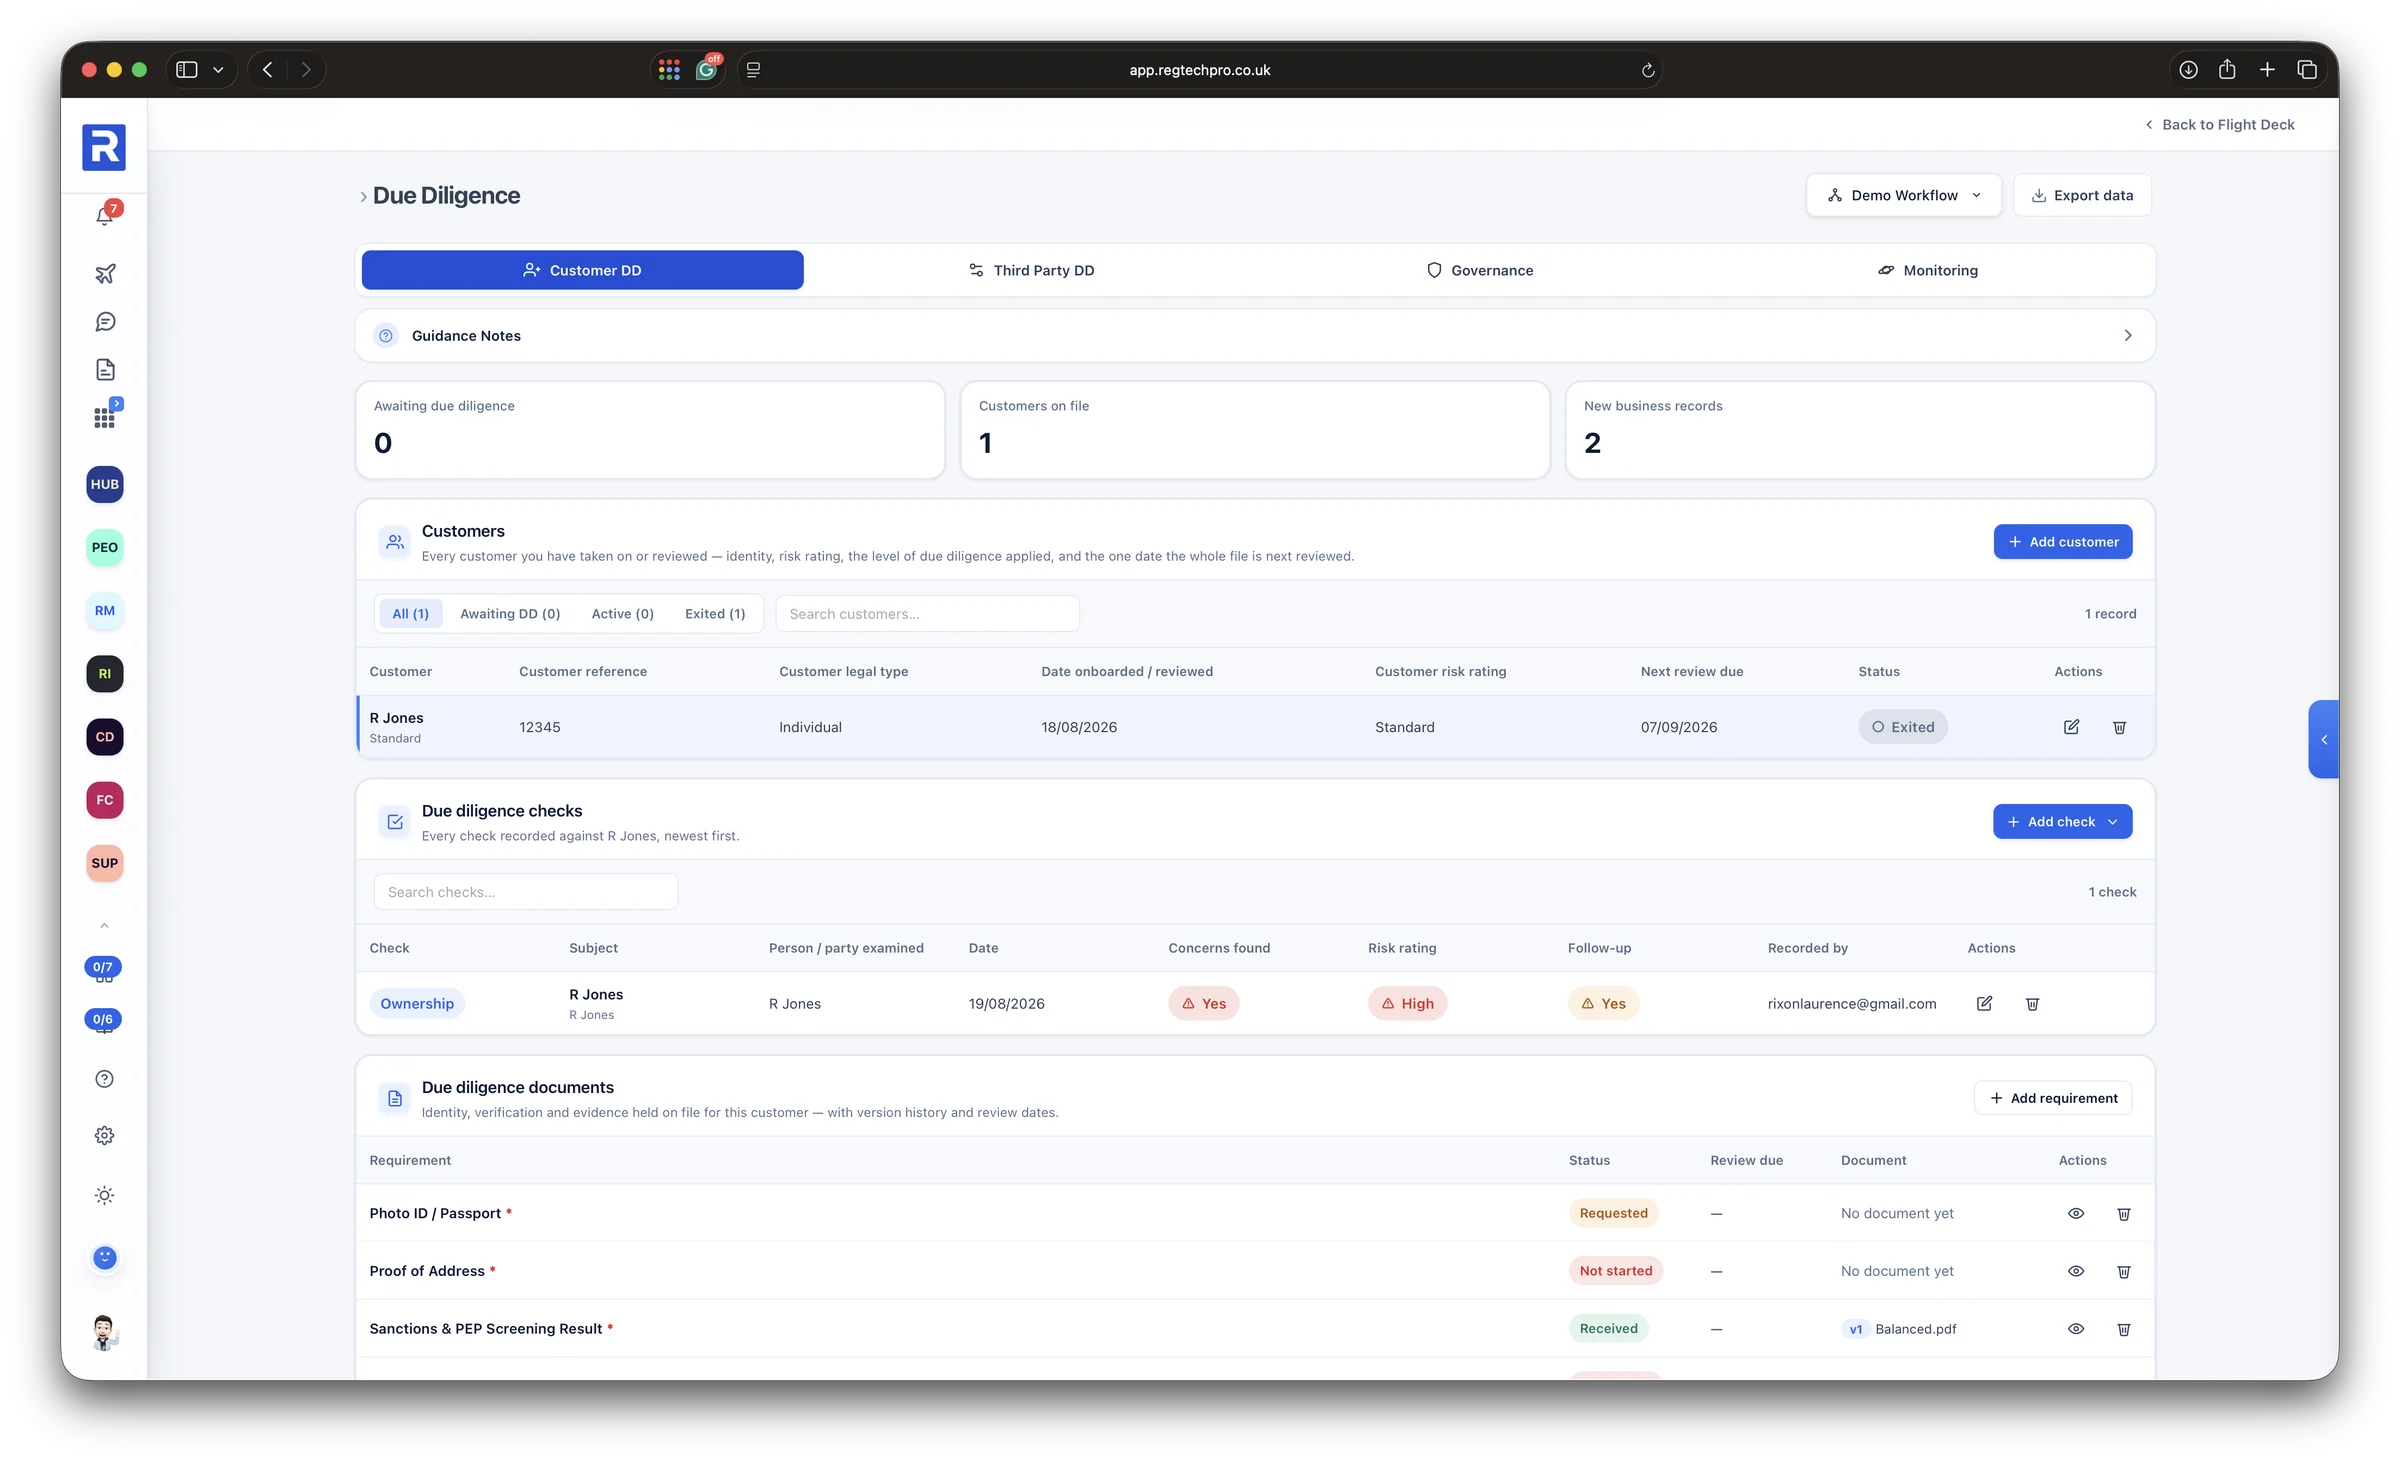
Customer and third-party due diligence, on registers of your own
Twenty-three due-diligence registers that belong to the module outright. On the customer side: reviews, beneficial ownership, client categorisation, enhanced due-diligence cases, exits, and screening split into sanctions, adverse media, criminal records and politically exposed persons so each can be run and dated separately. On the third-party side: investment platforms, providers and products, outsourcing arrangements and introducers and distributors, each with the same separate screening checks, recorded as they are done. Each record can be linked back to the New Business entry that raised it through a searchable dropdown — a reference, not a dependency, so removing the New Business entry never removes the due-diligence file. Each customer and third party carries one next review date for the whole file, and it feeds the overdue list.
Who it’s forFirms that onboard customers or rely on third parties — advisers, brokers, platforms and any firm with outsourcing, introducer or distribution arrangements to evidence.
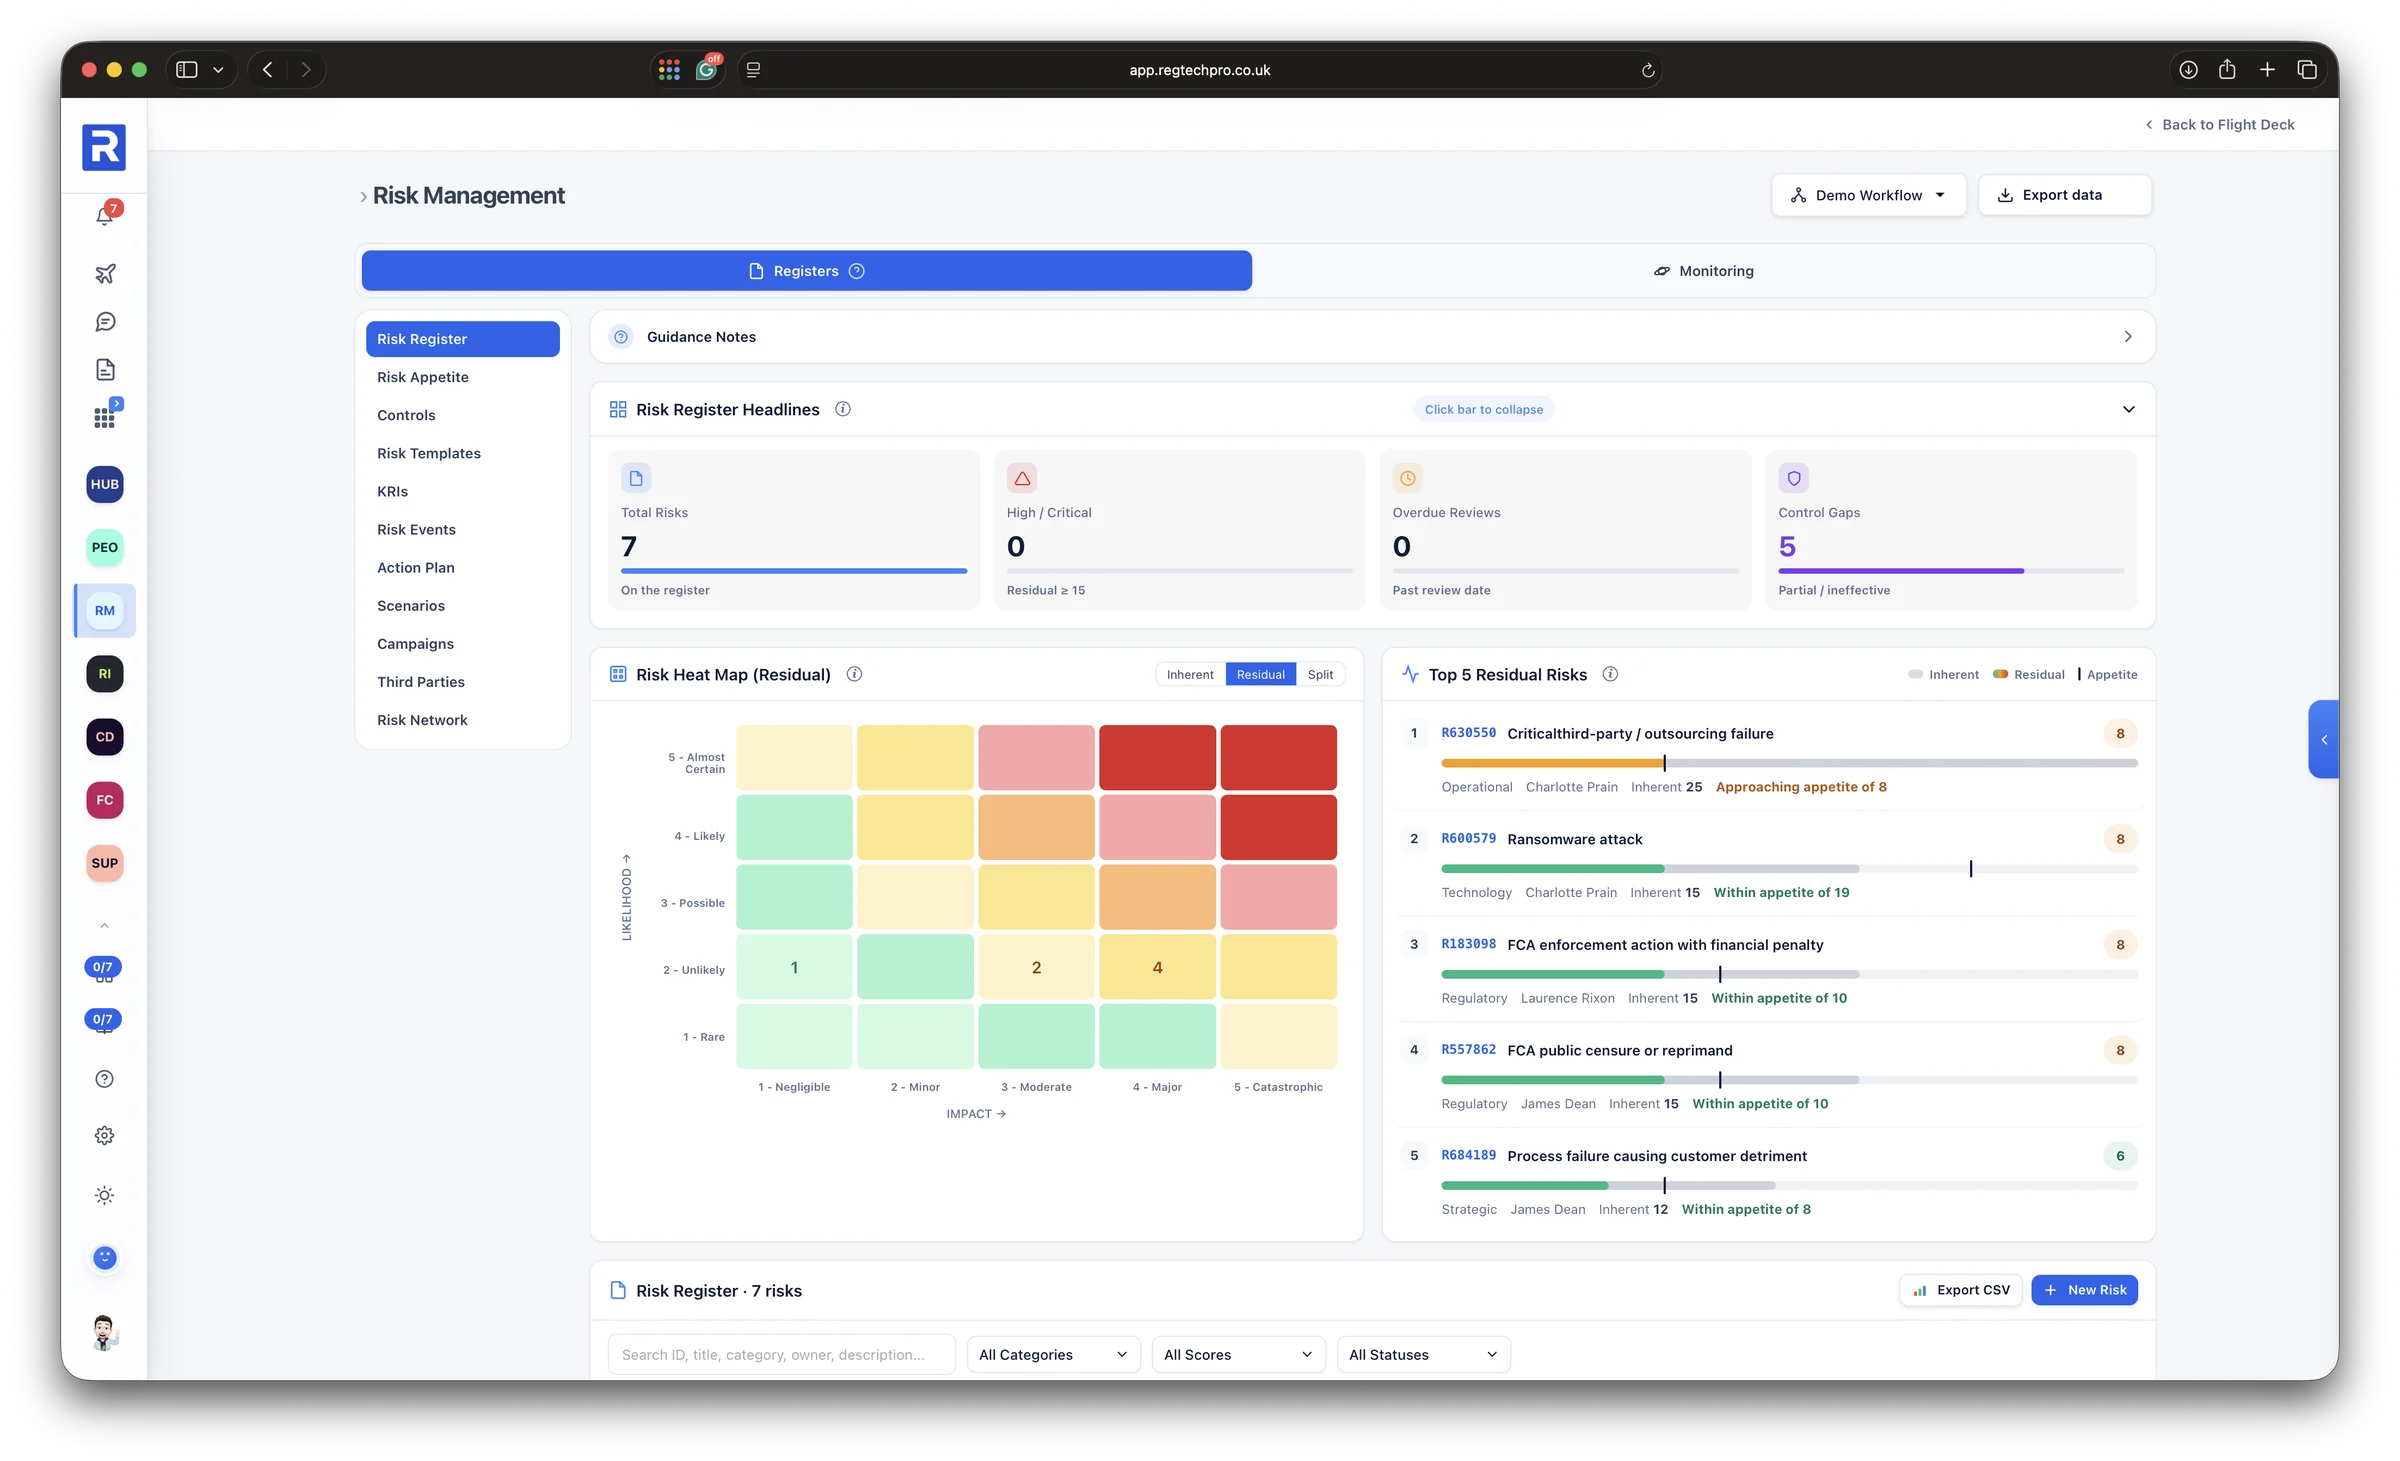
Enterprise-grade risk governance at SME pricing
An eleven-register FCA risk governance module built on a 5×5 register that scores inherent, residual and appetite separately, backed by mirrored controls, KRIs, loss events, action plans and stress scenarios. It adds a third-party register aligned to the Critical Third Parties regime, a force-directed risk network with concentration alerts, and RCSA attestation campaigns that produce signed-off, versioned audit snapshots. The Reports module builds a 15-section Risk Committee Report from the firm's live data, with Otto writing the commentary.
Who it’s forHeads of Risk, CROs and SMF holders at FCA-regulated firms, plus consultants and principals running multiple client or AR risk registers from one login.
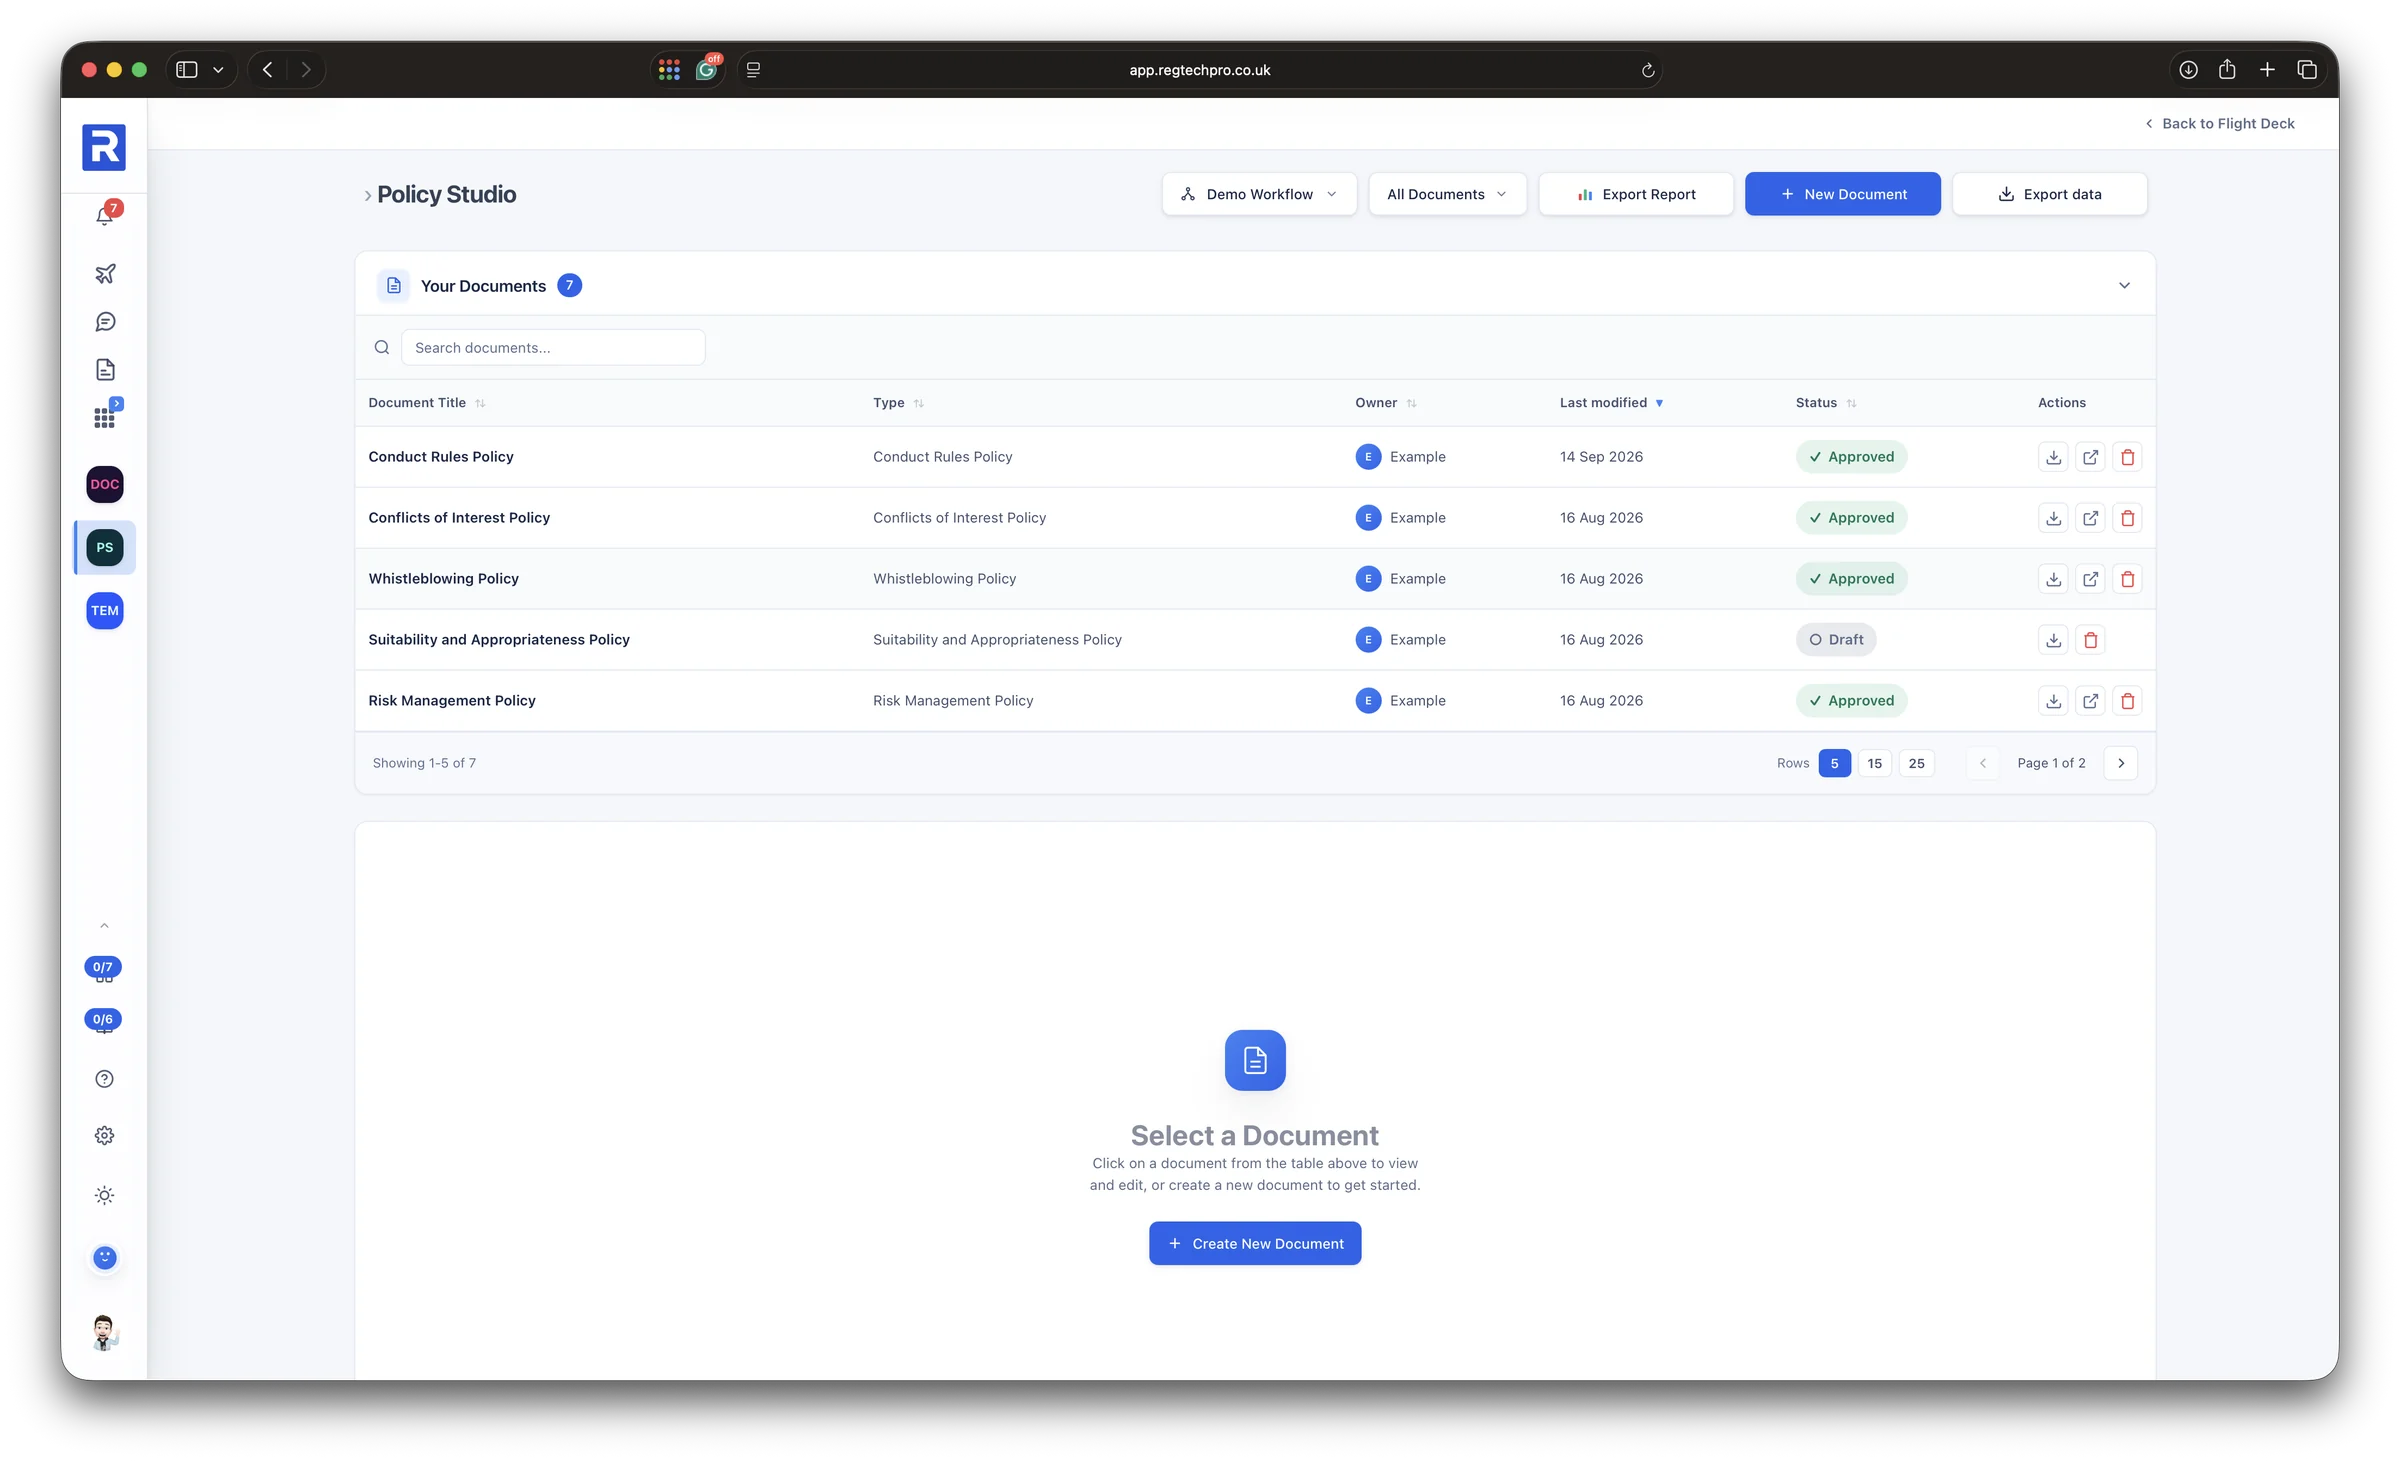
Drafts, reviews and operationalises every policy
A five-stage policy lifecycle that takes a document to FCA-ready evidence: start from a Template Vault document or your own upload, Otto assesses, improves or rewrites it, then turns its key commitments into tracked tasks. Each task quotes the policy wording it came from, so a written obligation ties to an evidenced operation. The finished library exports as a Policy Register PDF for supervisors.
Who it’s forFCA-regulated firms and compliance consultancies that need to draft, maintain, approve and evidence their policy suite without outsourcing to consultants.
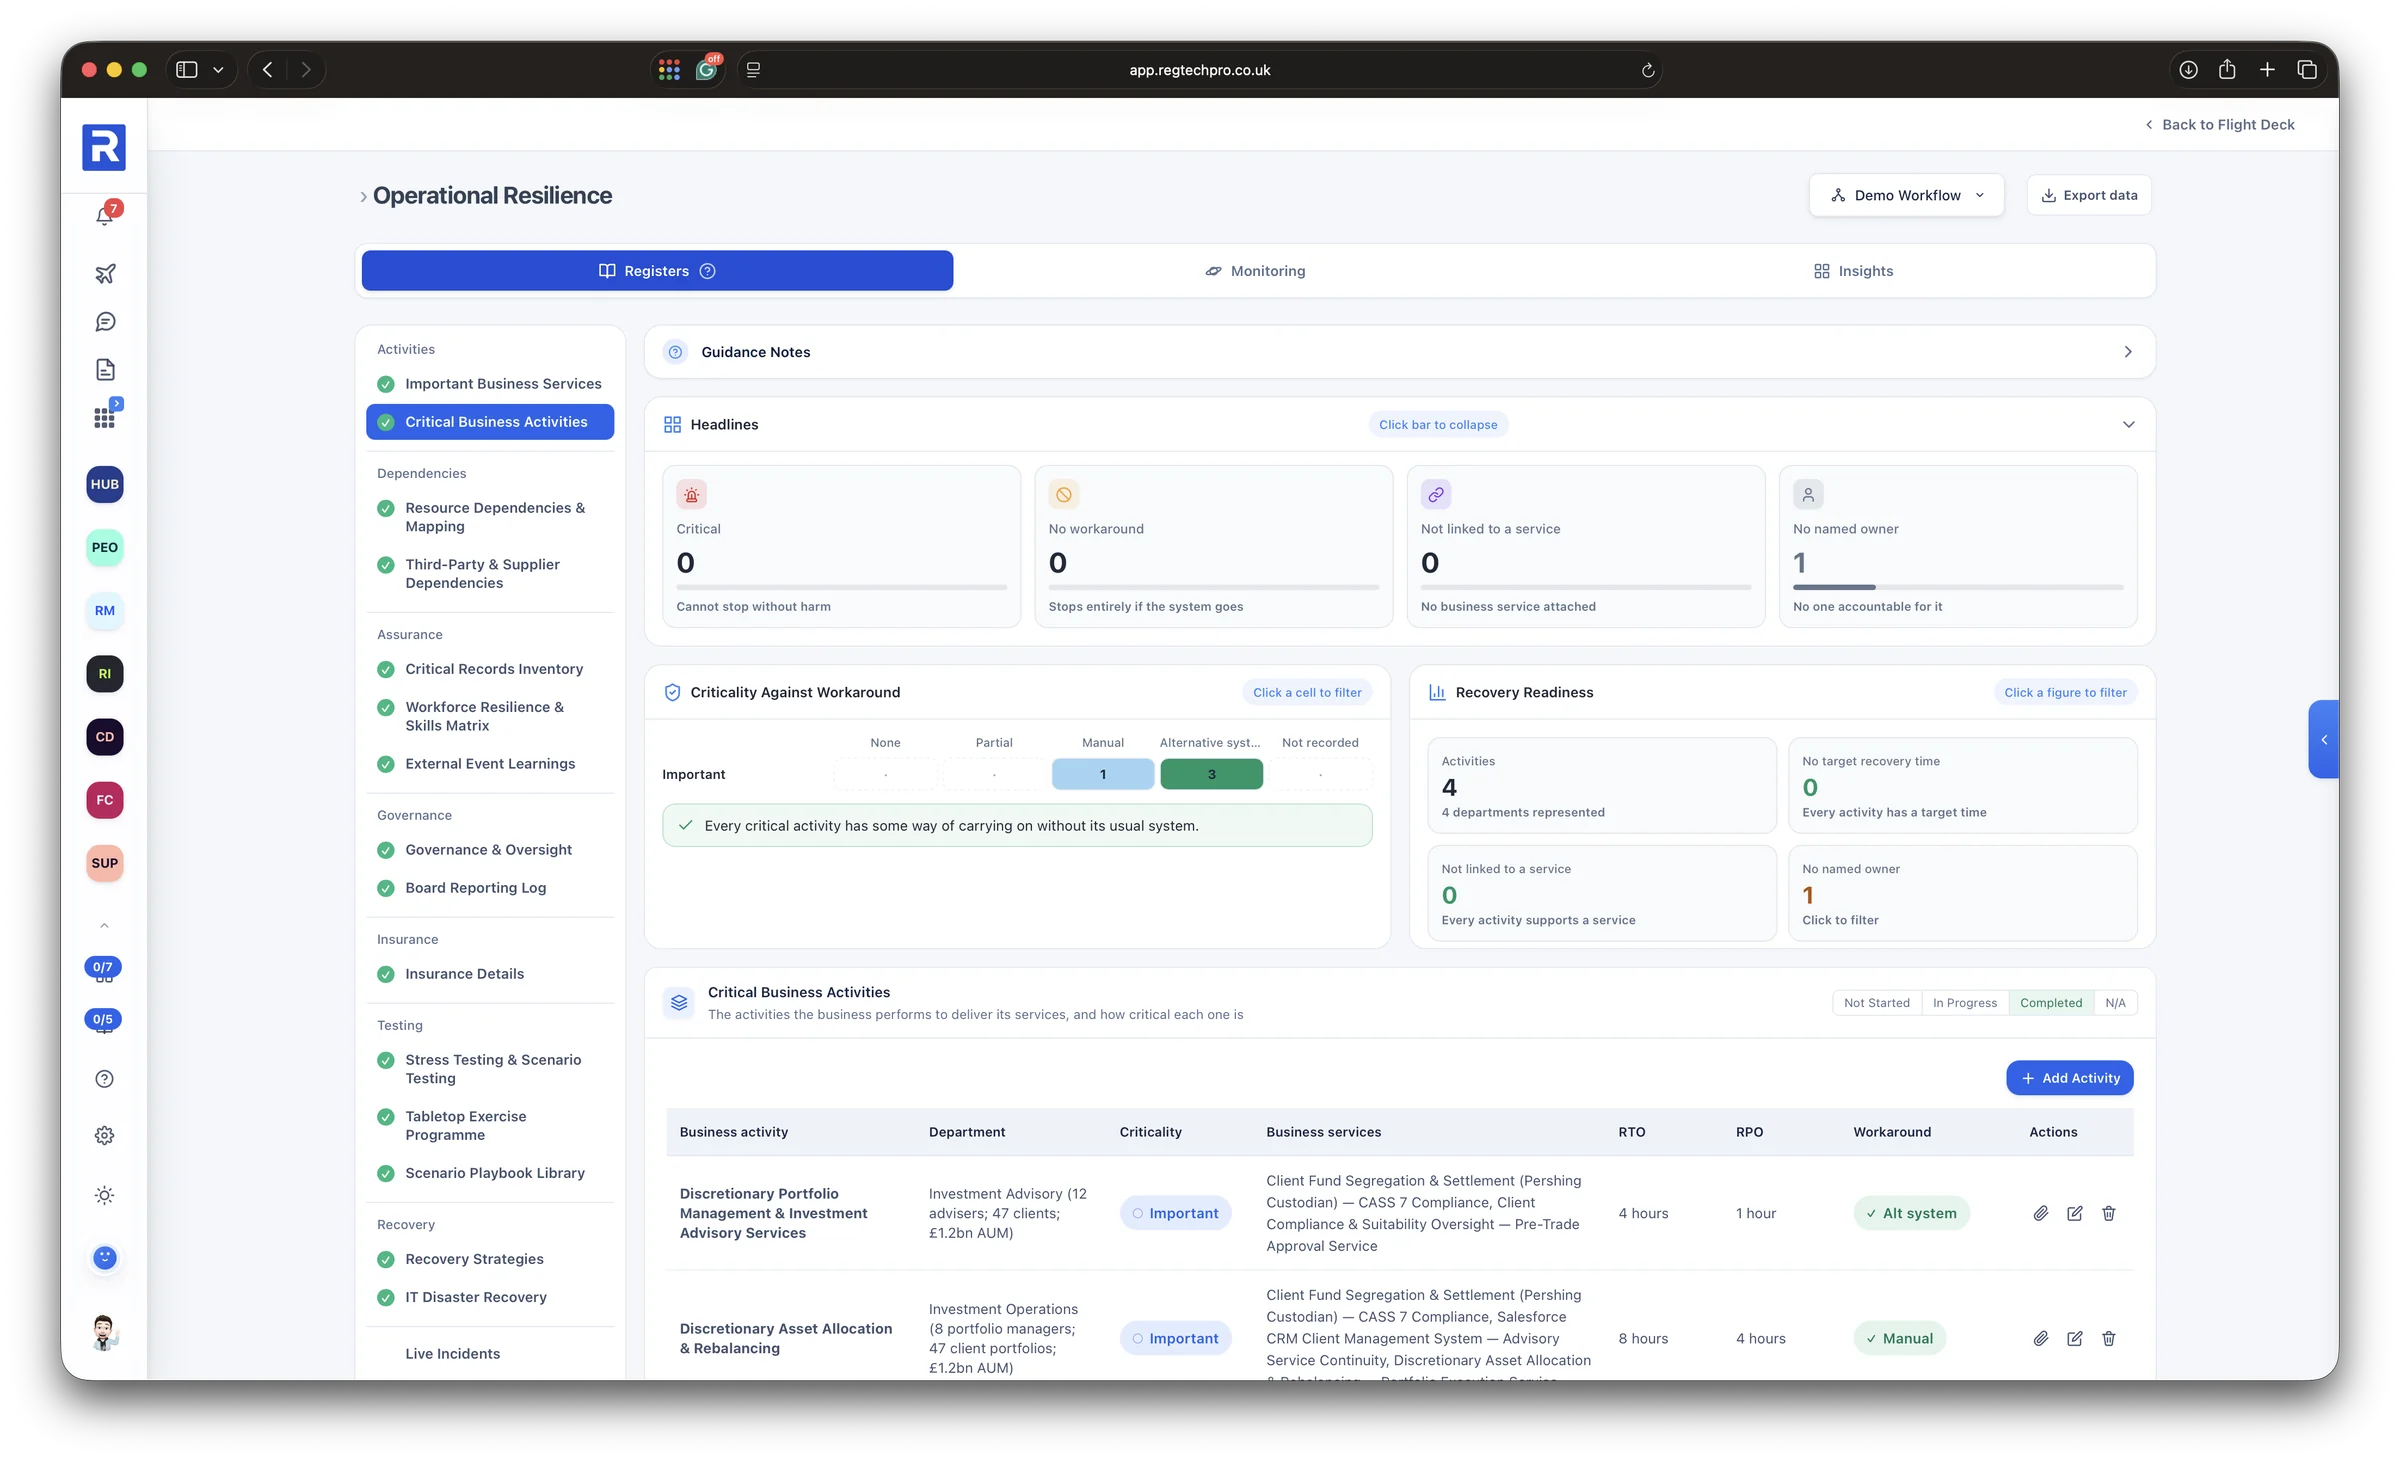
SYSC 15A resilience, from planning to live incident
A complete SYSC 15A operational-resilience system covering the full programme: business impact analysis, dependency mapping, recovery planning, live incident management and board-ready reporting. A Resilience Health Score measures how complete the programme is across every register, attestation and monitoring check, so the number shows what is actually done. Incident Mode runs a live FCA 4-hour notification countdown during a real disruption, and every closed incident auto-feeds the stress-testing register.
Who it’s forFor Heads of Operational Resilience, COOs and BCP coordinators at FCA-authorised firms meeting SYSC 15A obligations — from proportionate small-firm BCP through to full PS21/3 enhanced scope.
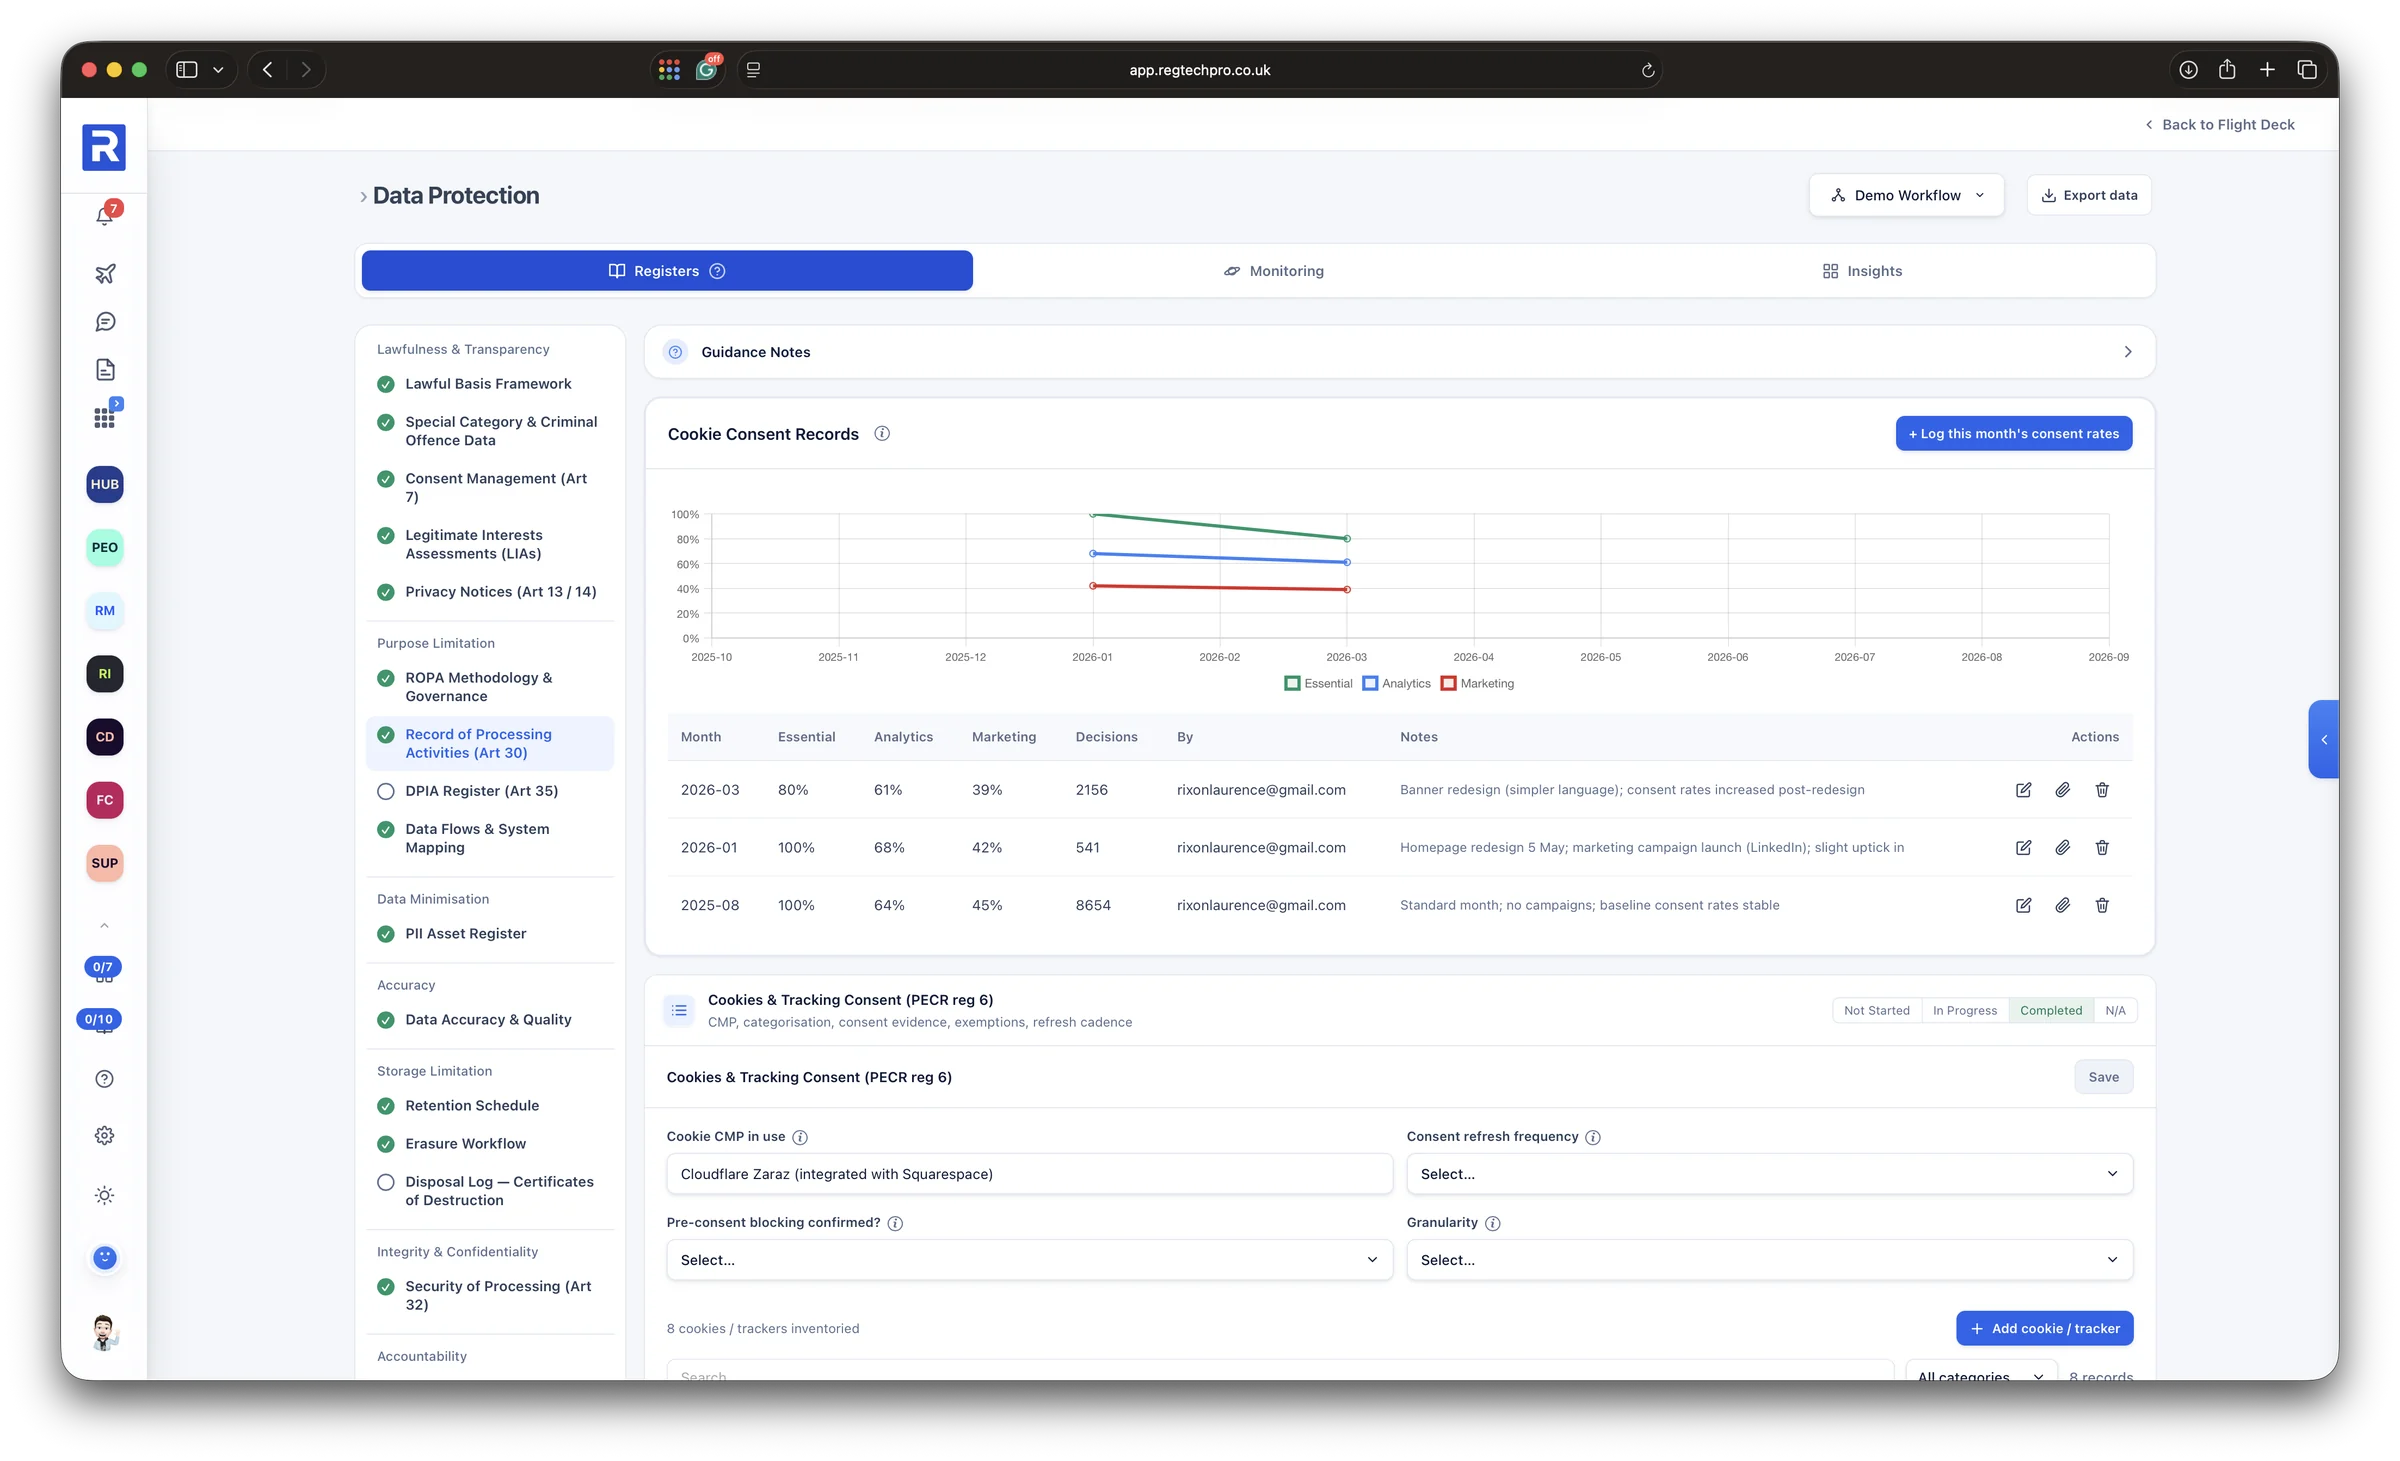
When the ICO calls, every answer is ready
A UK GDPR, DPA 2018 and PECR operating layer for the data protection officer. It runs the working registers — ROPA, data-subject rights, breaches, DPIAs and international transfers — and measures how complete the programme is across its registers, attestation and monitoring checks. A live 72-hour breach clock and reports in the Reports module keep the DPO audit-ready.
Who it’s forAny firm processing personal data, run by the DPO or whoever carries data-protection responsibility; for FCA firms it also meets SYSC 3.2.20.
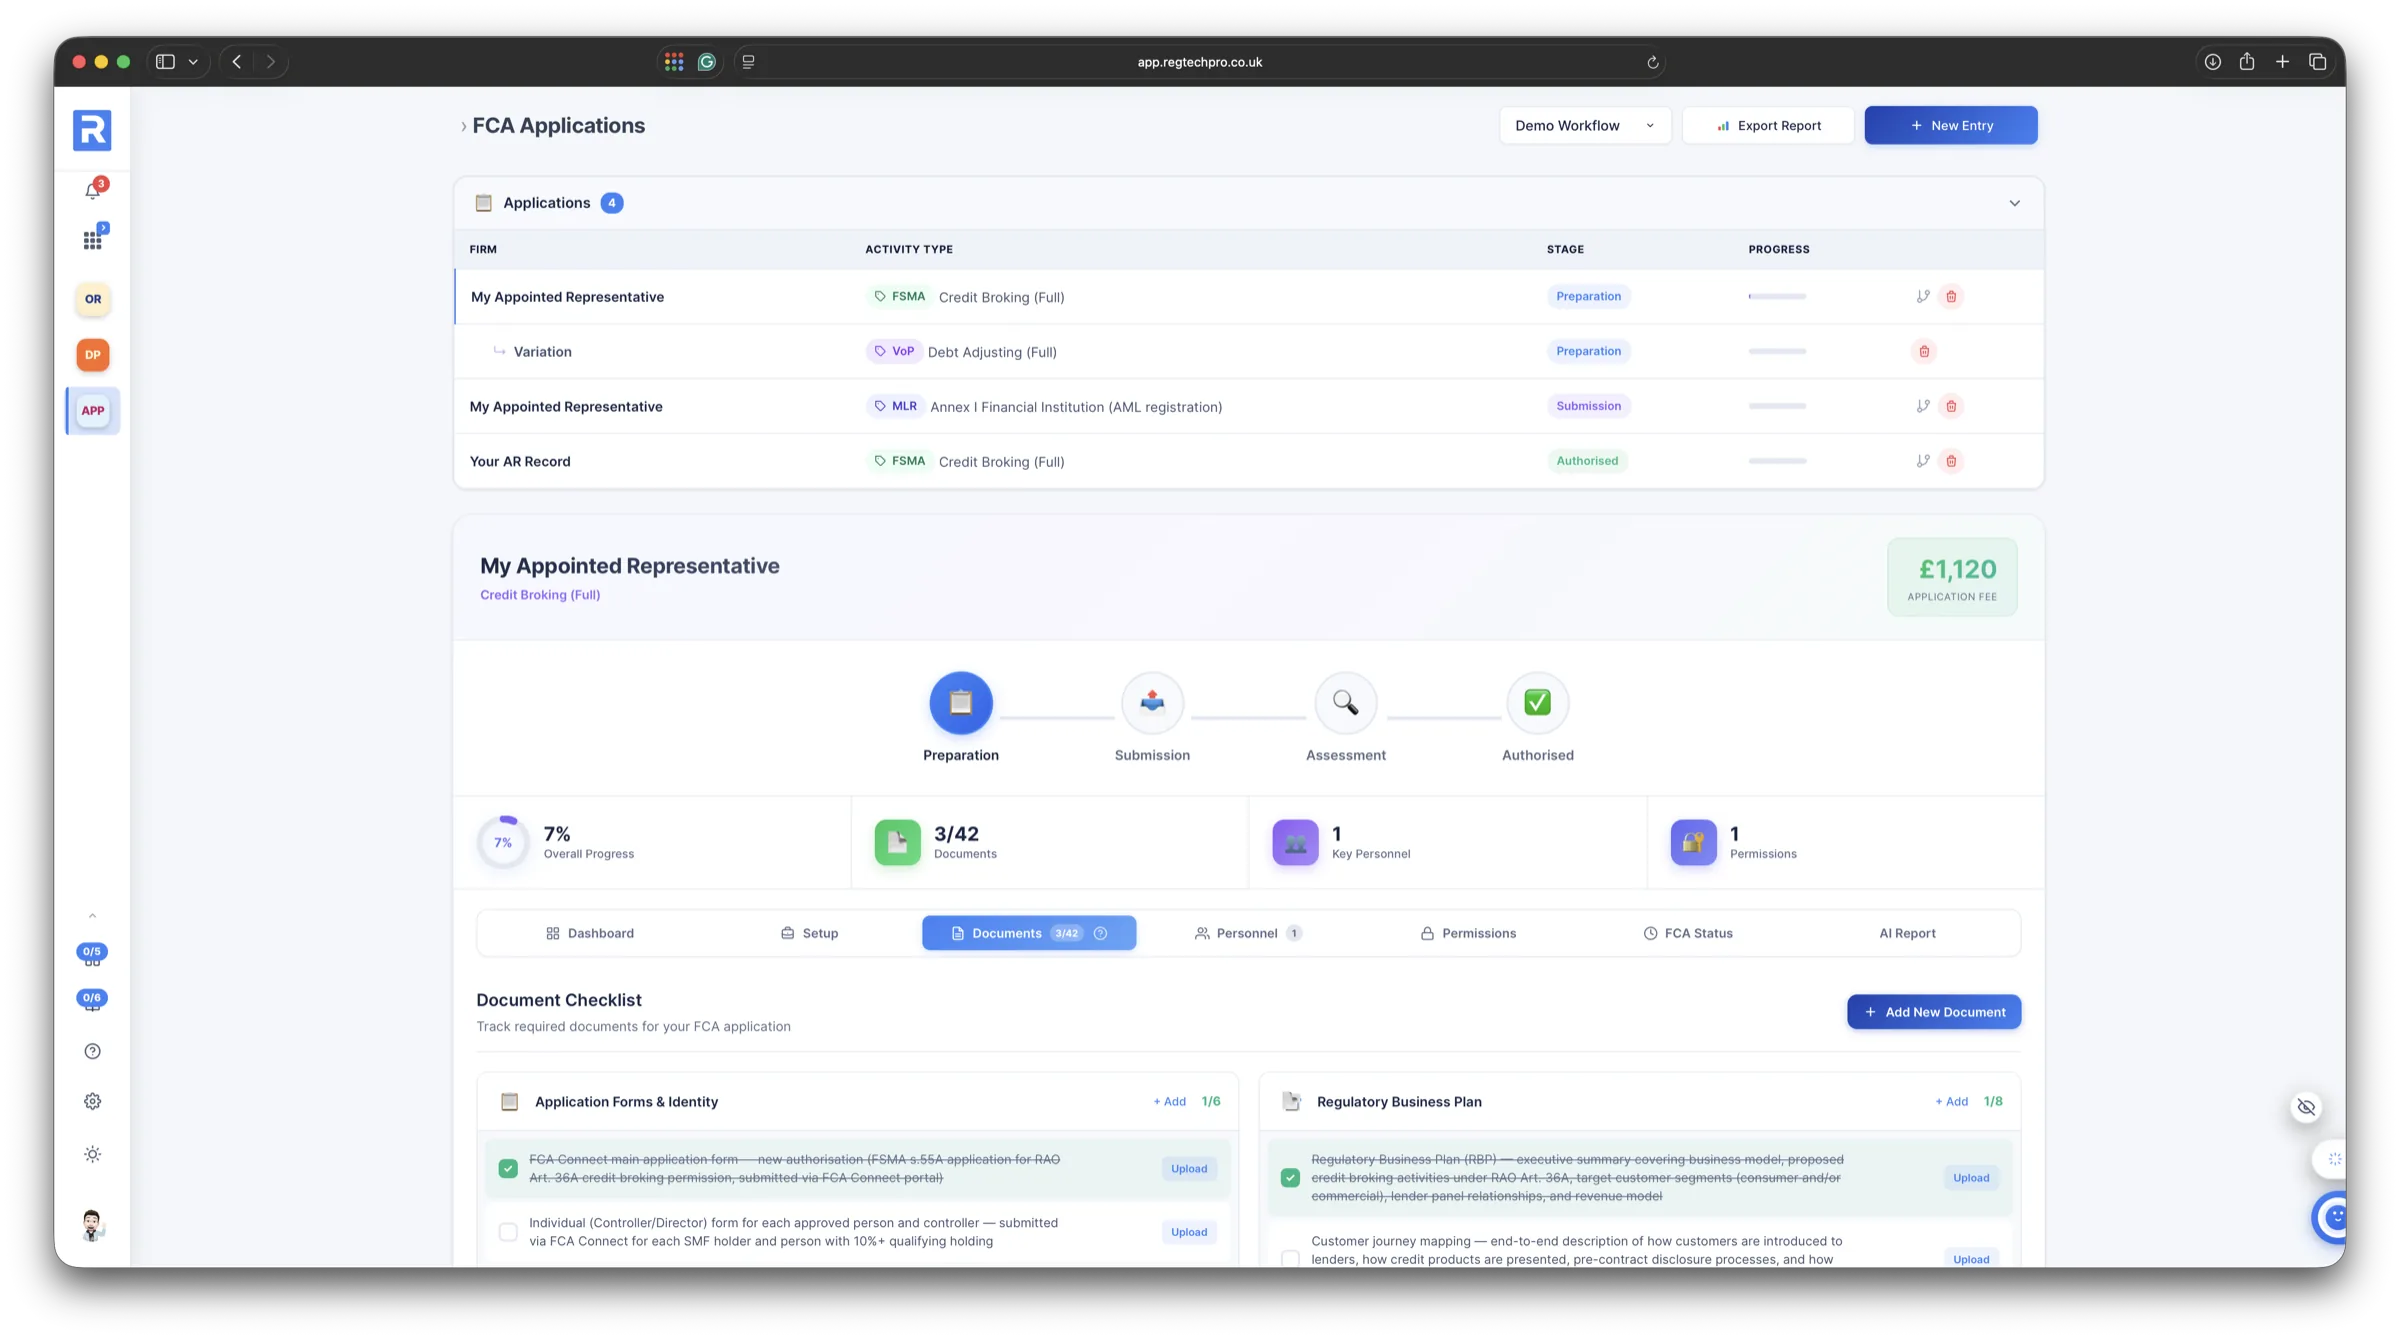
From first draft to FCA authorisation
A guided FCA authorisation and MLR registration tracker. Pick a regulated activity and Otto generates an 8-section requirements blueprint and an activity-scoped document checklist against live FCA guidance, then you work the application through a 4-stage lifecycle with a live 180-day assessment countdown. Variations of permission run as a linked path off the original application, so the full history is kept.
Who it’s forFirms preparing an FCA authorisation, variation of permission or MLR registration — and consultancies running applications for multiple client firms.
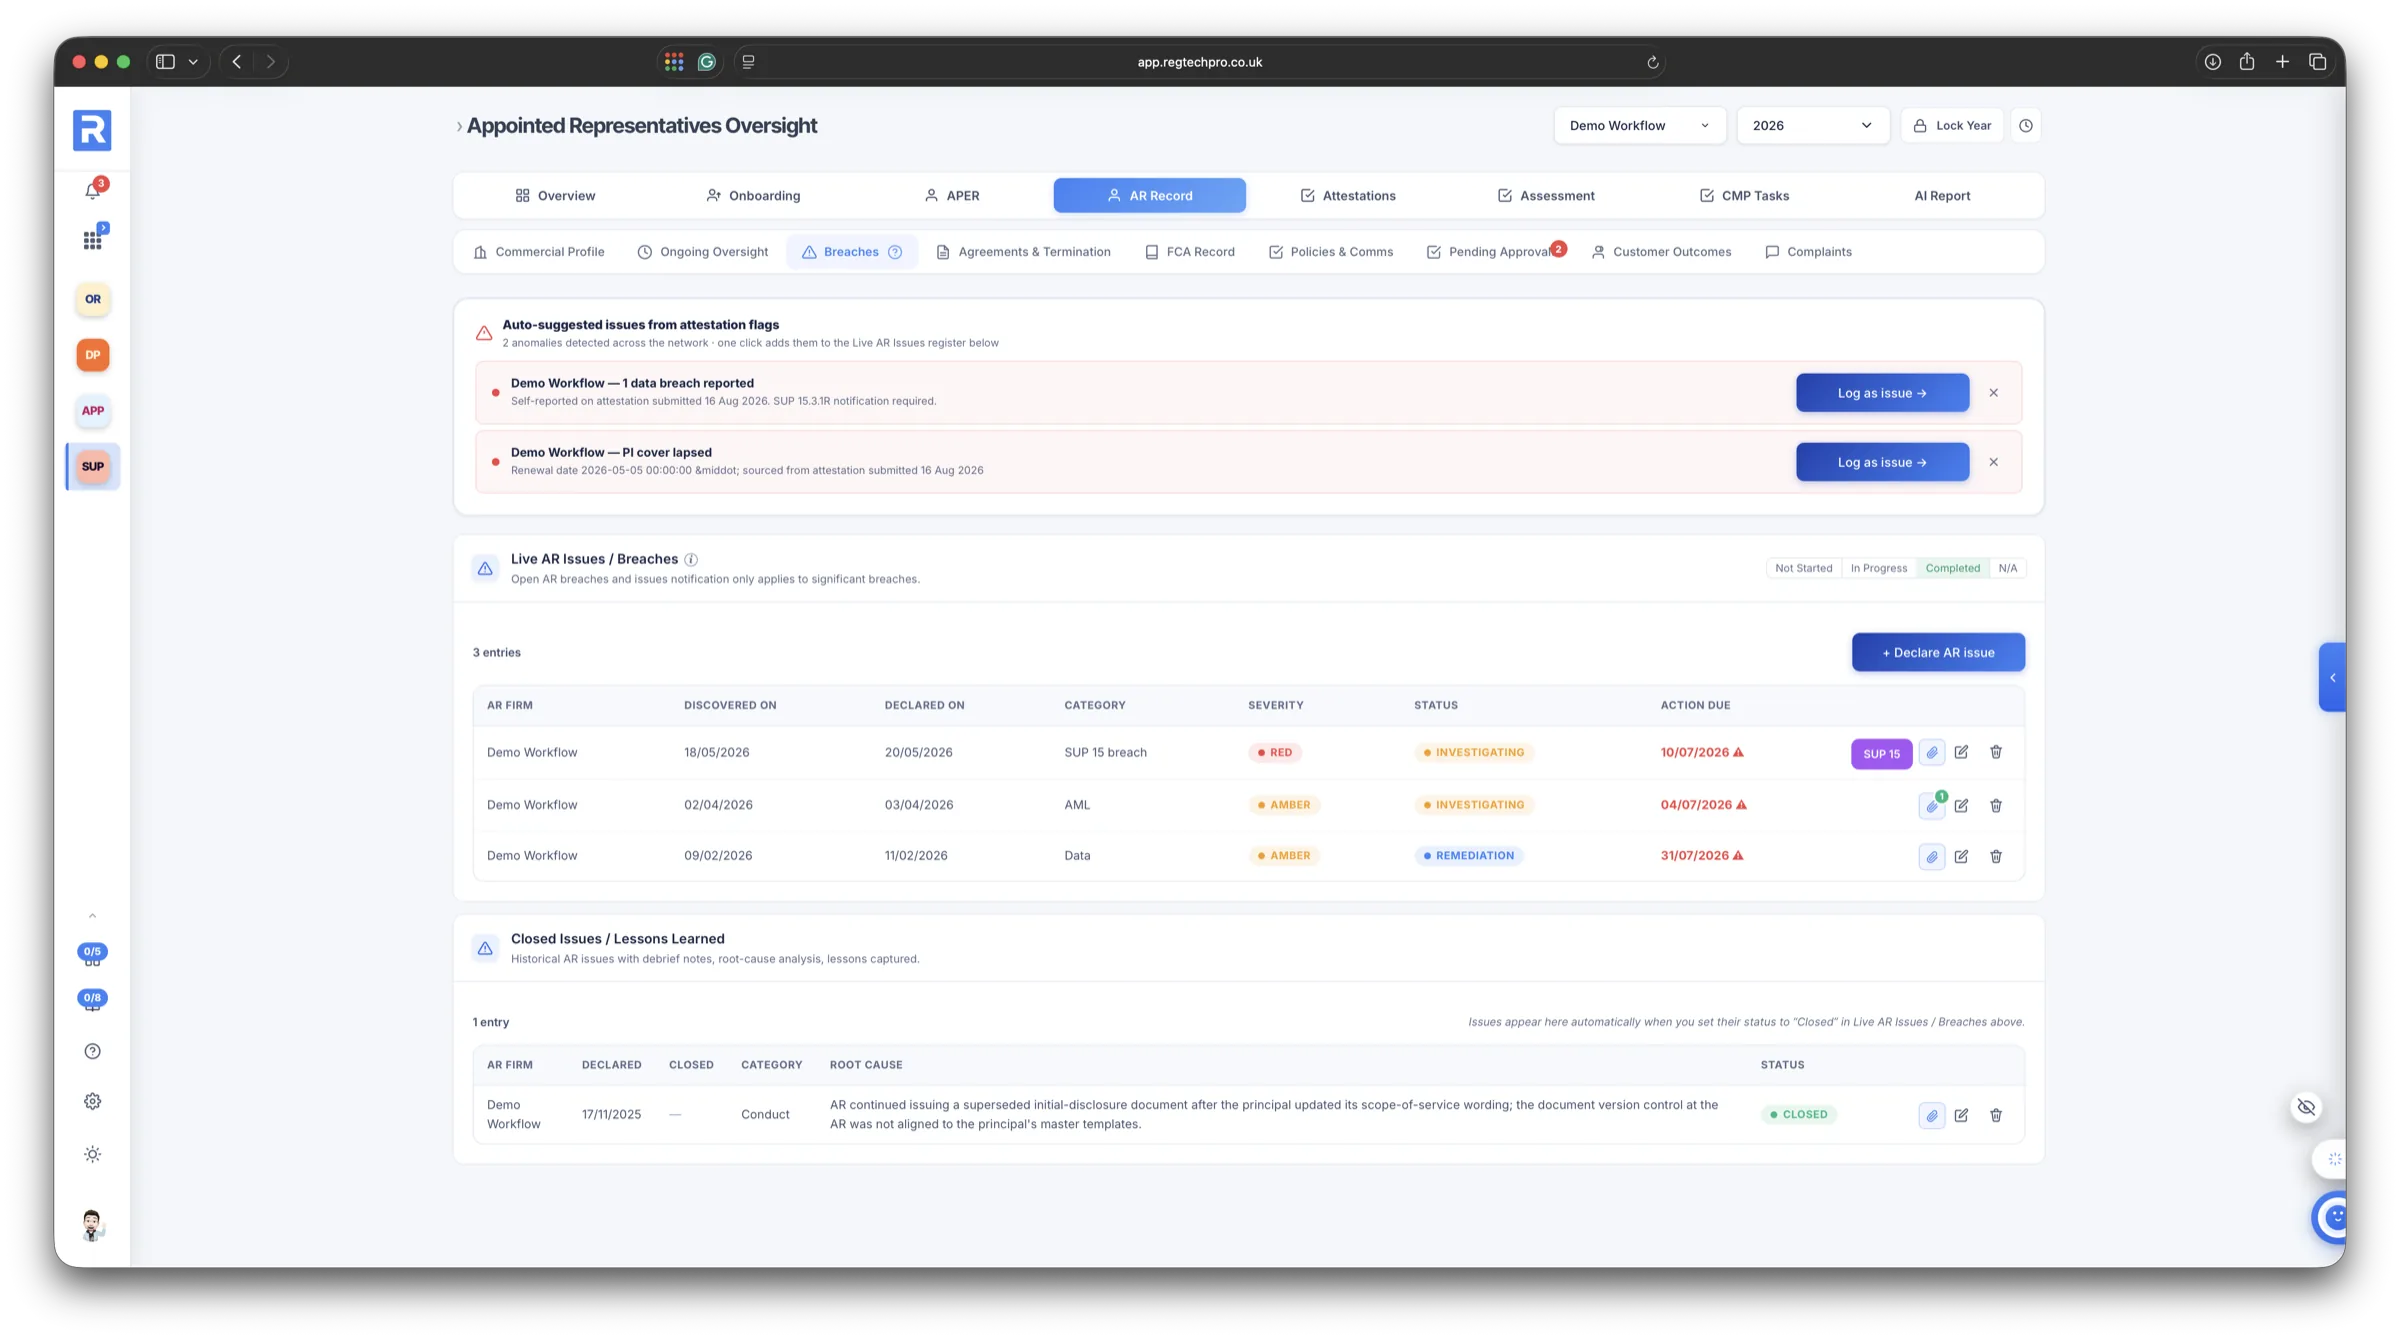
The operating system for appointed-representative oversight
A complete operating layer for FCA SUP 12 oversight of appointed representatives, built for the post-Dec 2022 enhanced regime and the 2024 FCA Multi-Firm Review of principal firms. Each AR gets its own onboarding, due-diligence, monitoring and annual-review record, scored on completion across registers, attestations and monitoring checks, and rolled up into a network view. The Reports module builds a full SUP 12 Report and an FCA Readiness mock supervisory interview from your live records.
Who it’s forFCA-authorised principal firms supervising appointed representatives or IARs — IFA, wealth, mortgage, consumer-credit and insurance intermediary networks.
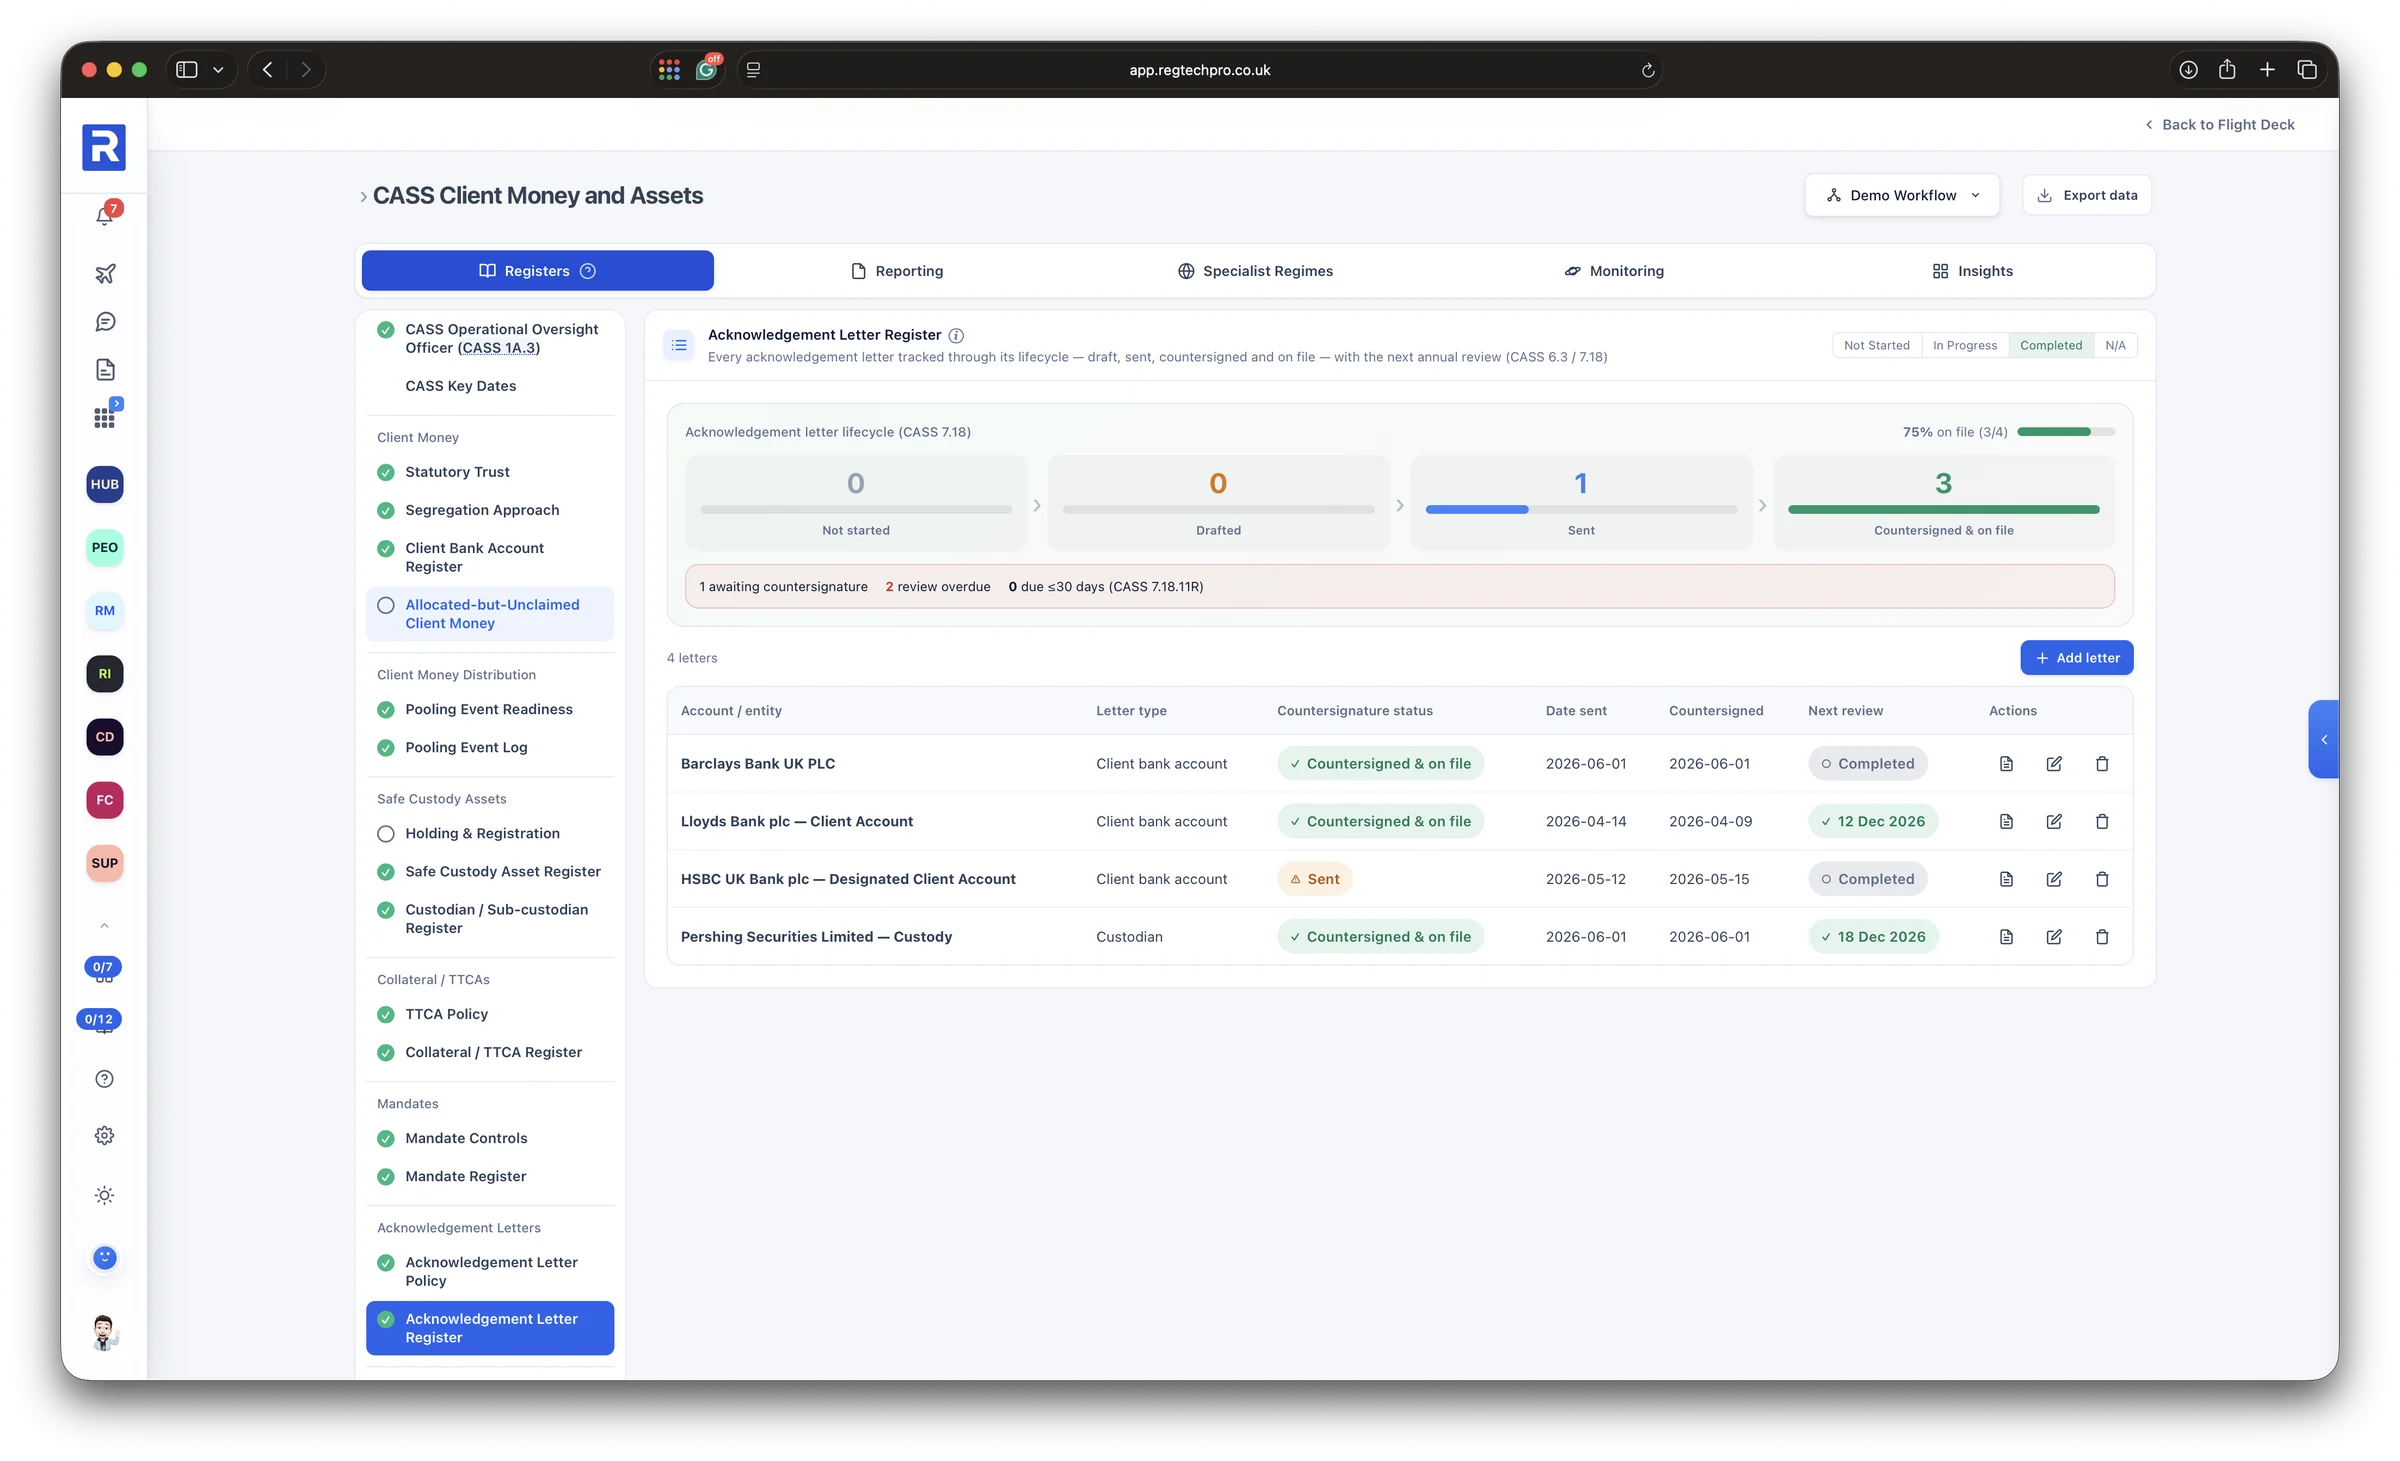
The FCA Client Assets sourcebook as an operating system
Turns the FCA Client Assets sourcebook into structured registers, calculators, reconciliation engines and evidence, covering the 14 CASS chapters (1A–15) plus SUP 3.10 audit prep. A CASS 1 applicability engine switches on only the chapters that bind your firm by type, and a Client Assets Health score tracks completion across every register, attestation and monitoring check. It replaces CASS spreadsheets, much of a CASS-consultant retainer and the bulk of annual CASS-audit preparation.
Who it’s forFCA-regulated firms that hold or control client money or safe custody assets, and the CASS oversight officer (CASS 1A.3) accountable for them.
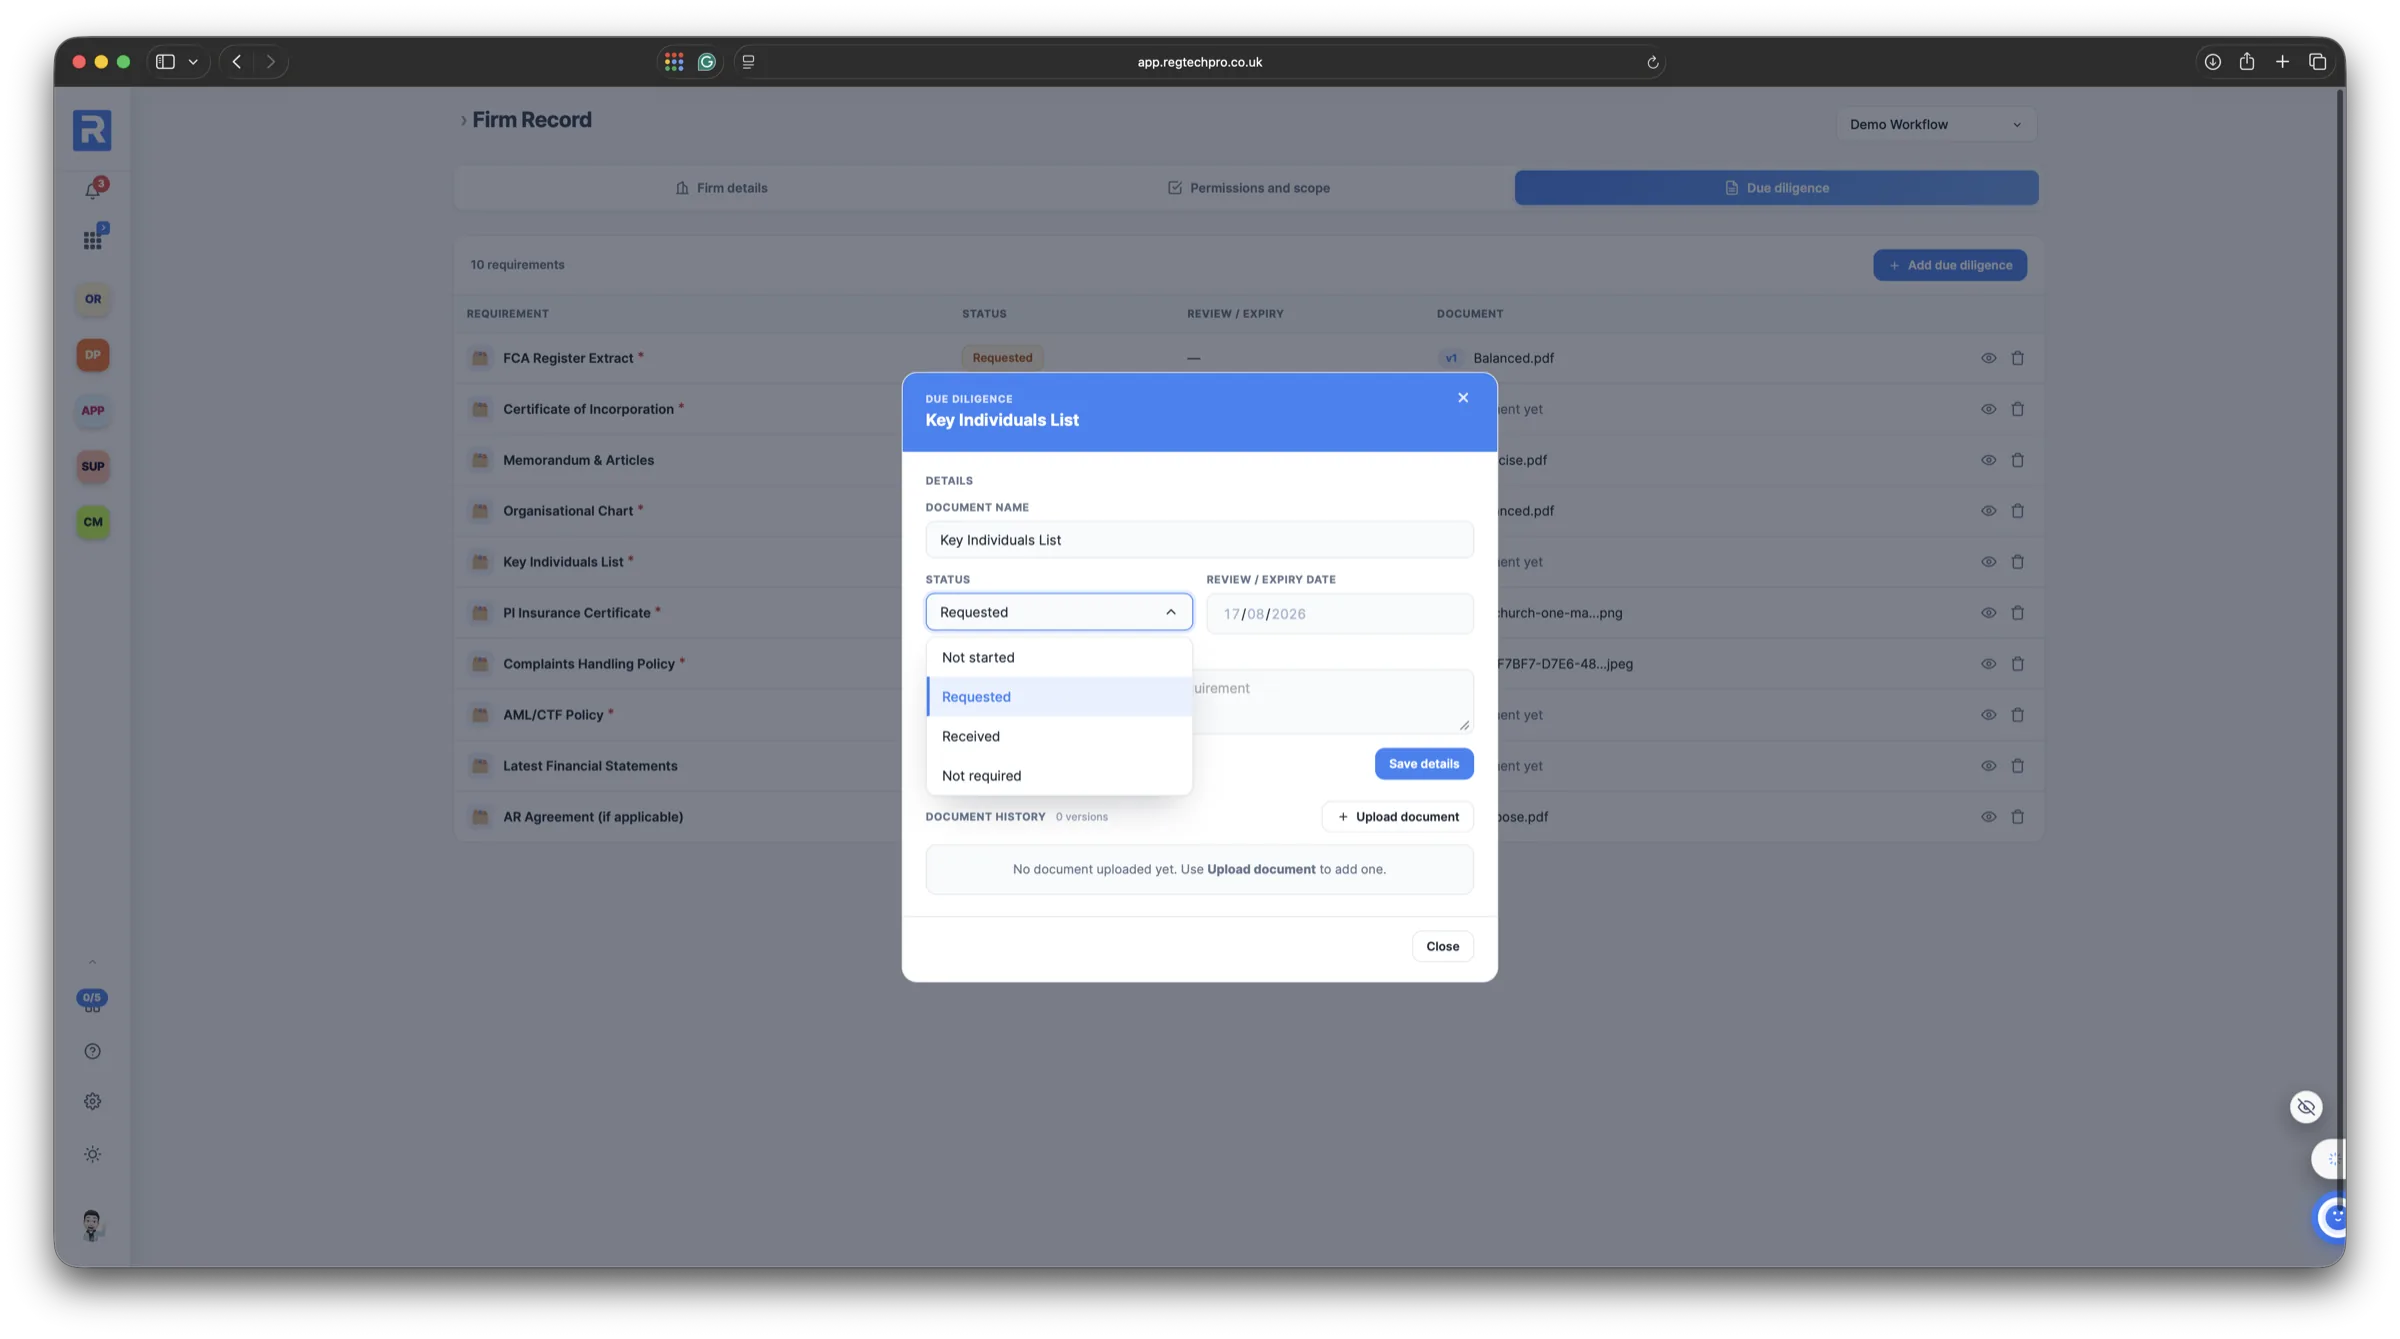
Your firm’s identity, permissions and due diligence, on file
One record per firm, holding the things every principal, auditor and regulator asks for about the firm itself: registered and trading name, FRN and company number, contact details and addresses, and a description of what the firm actually does. Beside it sit the two things nobody usually has written down — every regulated activity with its customer type, limitation and effective date, and a due-diligence file that versions each document and derives its own status from the review date.
Who it’s forEvery firm on the platform. Directly authorised firms keep one record; principals keep one per appointed representative; consultancies keep one per client firm.
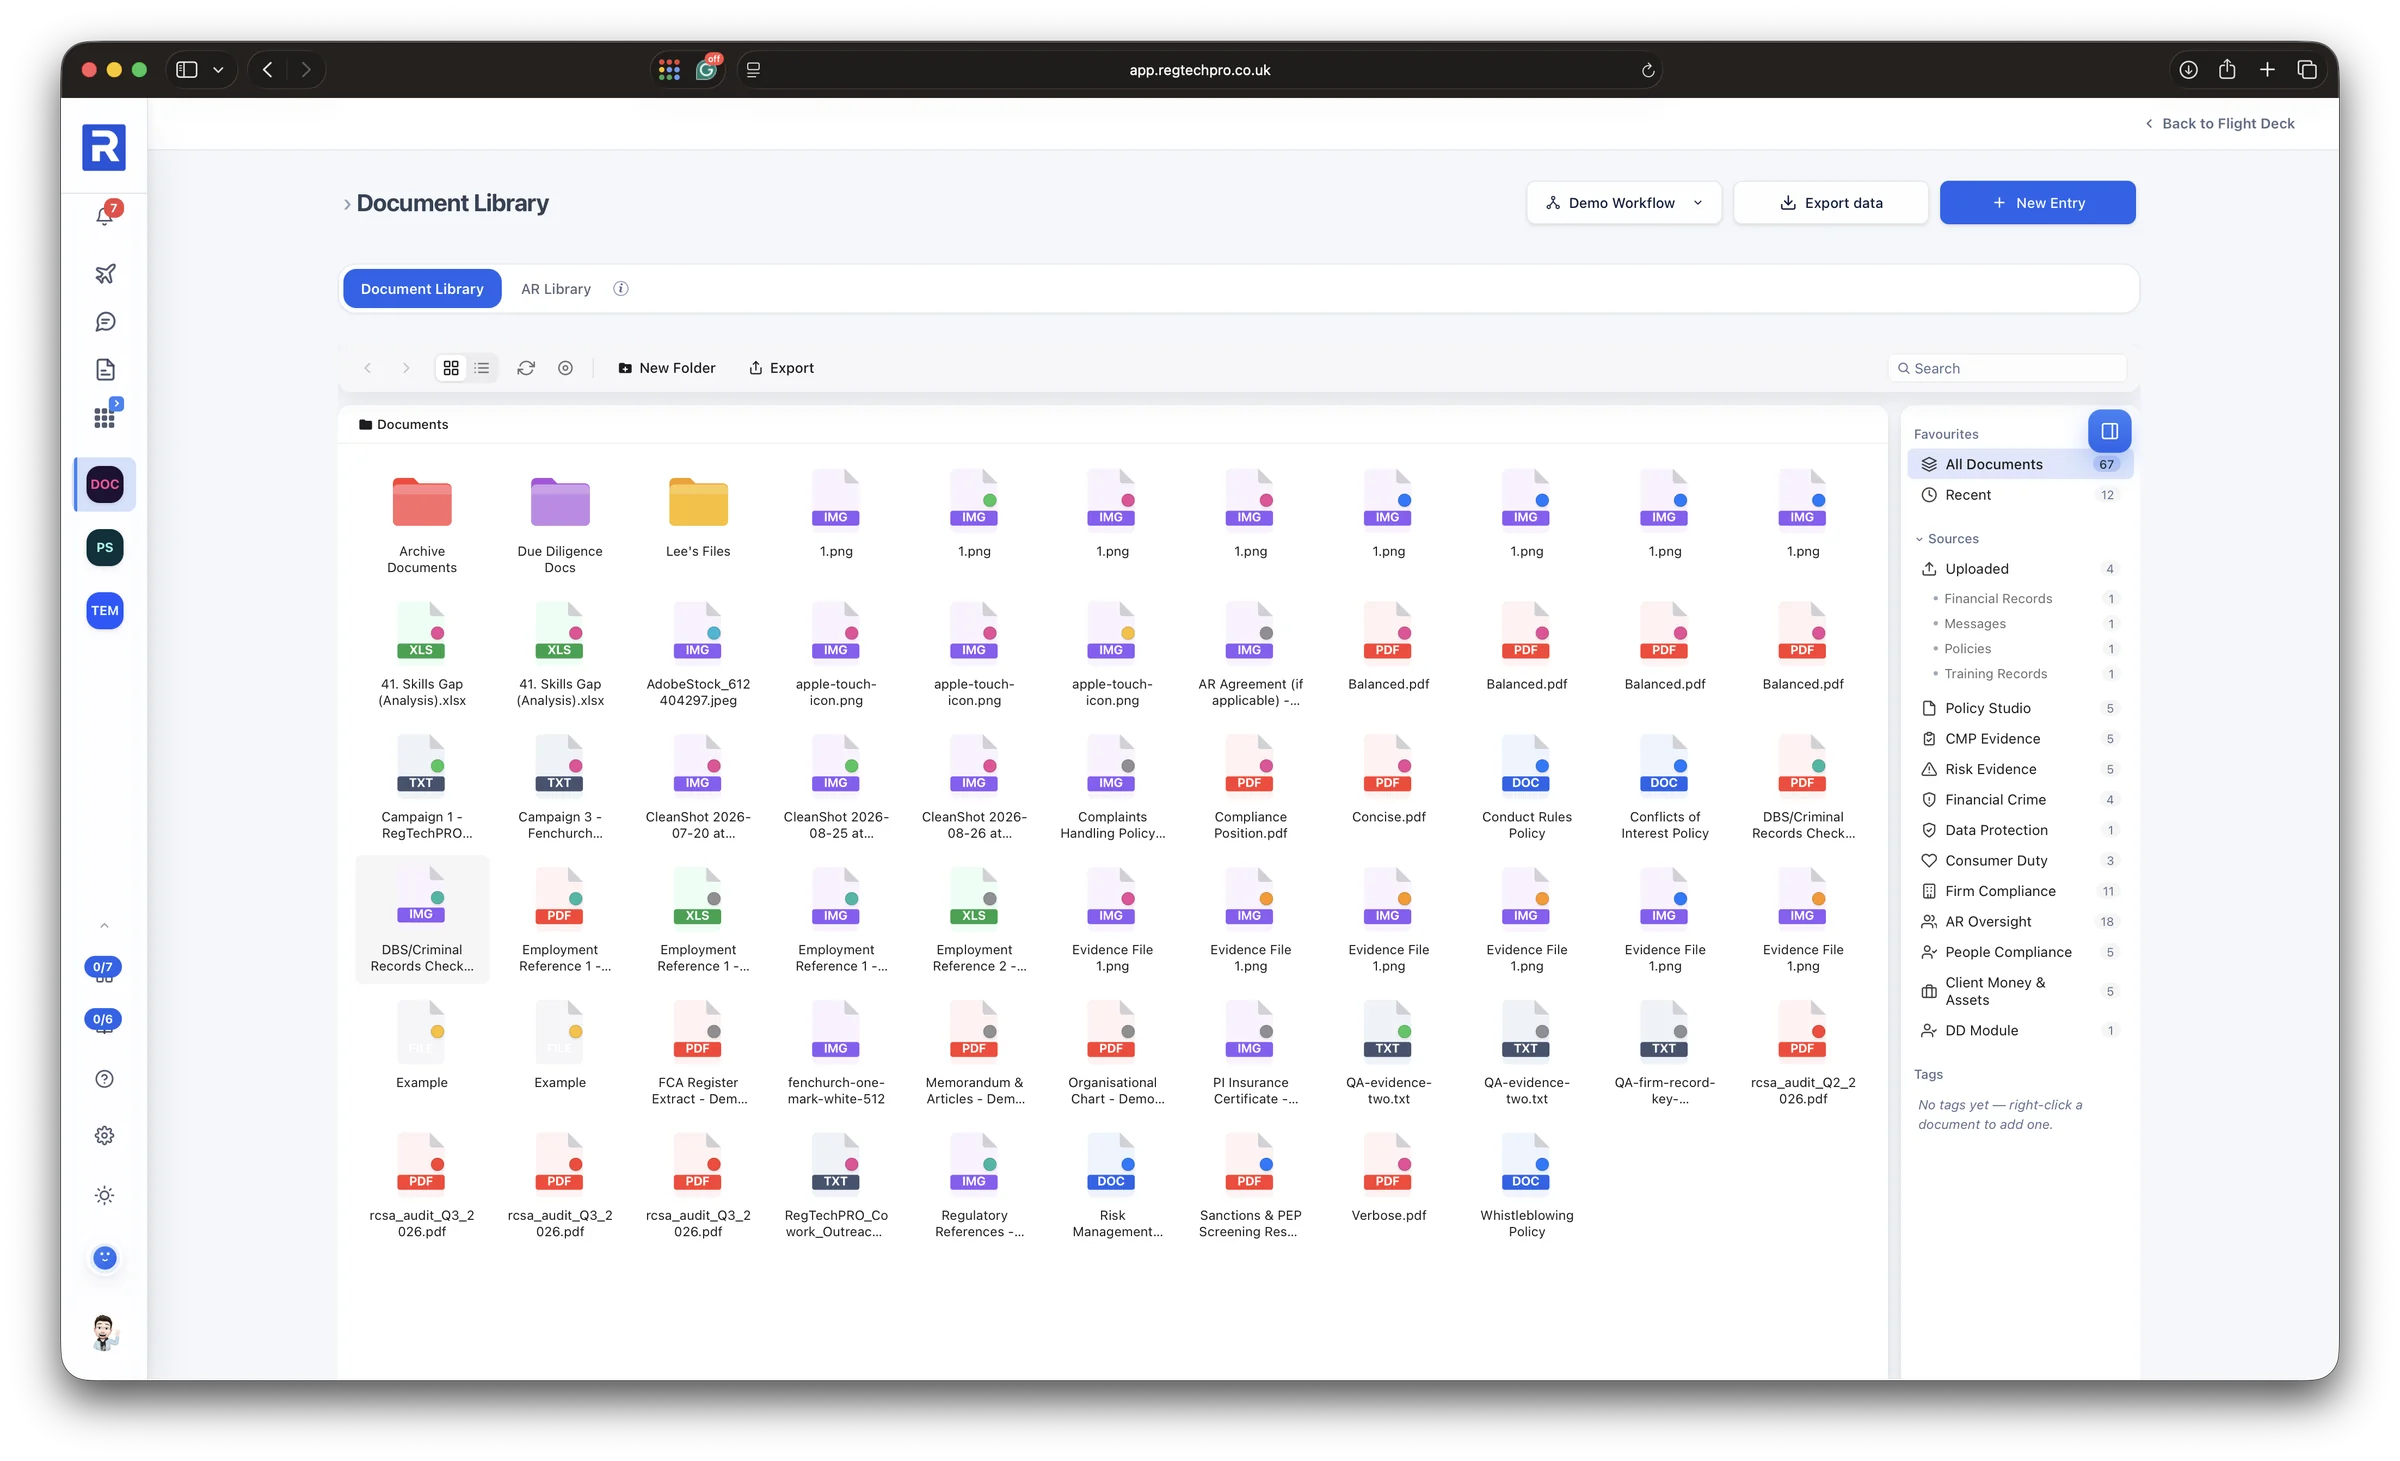
Every document the firm holds, filed as the work happens
A file browser for the firm’s evidence — folders, icon and list views, search, tags and export — with one difference that matters: it fills itself. When a module records a document, a copy is filed here under the name of the module that produced it, so the library is complete without anyone maintaining it. Documents are held centrally, and policies written in Policy Studio open in the full Google Docs editor, with the revision history an auditor will ask for and no Google subscription of your own to buy. A second tab holds the AR Library: only what a principal has deliberately shared with an appointed representative, plus that representative’s own uploads.
Who it’s forEvery firm on the platform. Principals get the second library for sharing a defined document set with each appointed representative, without opening up the rest of the file.
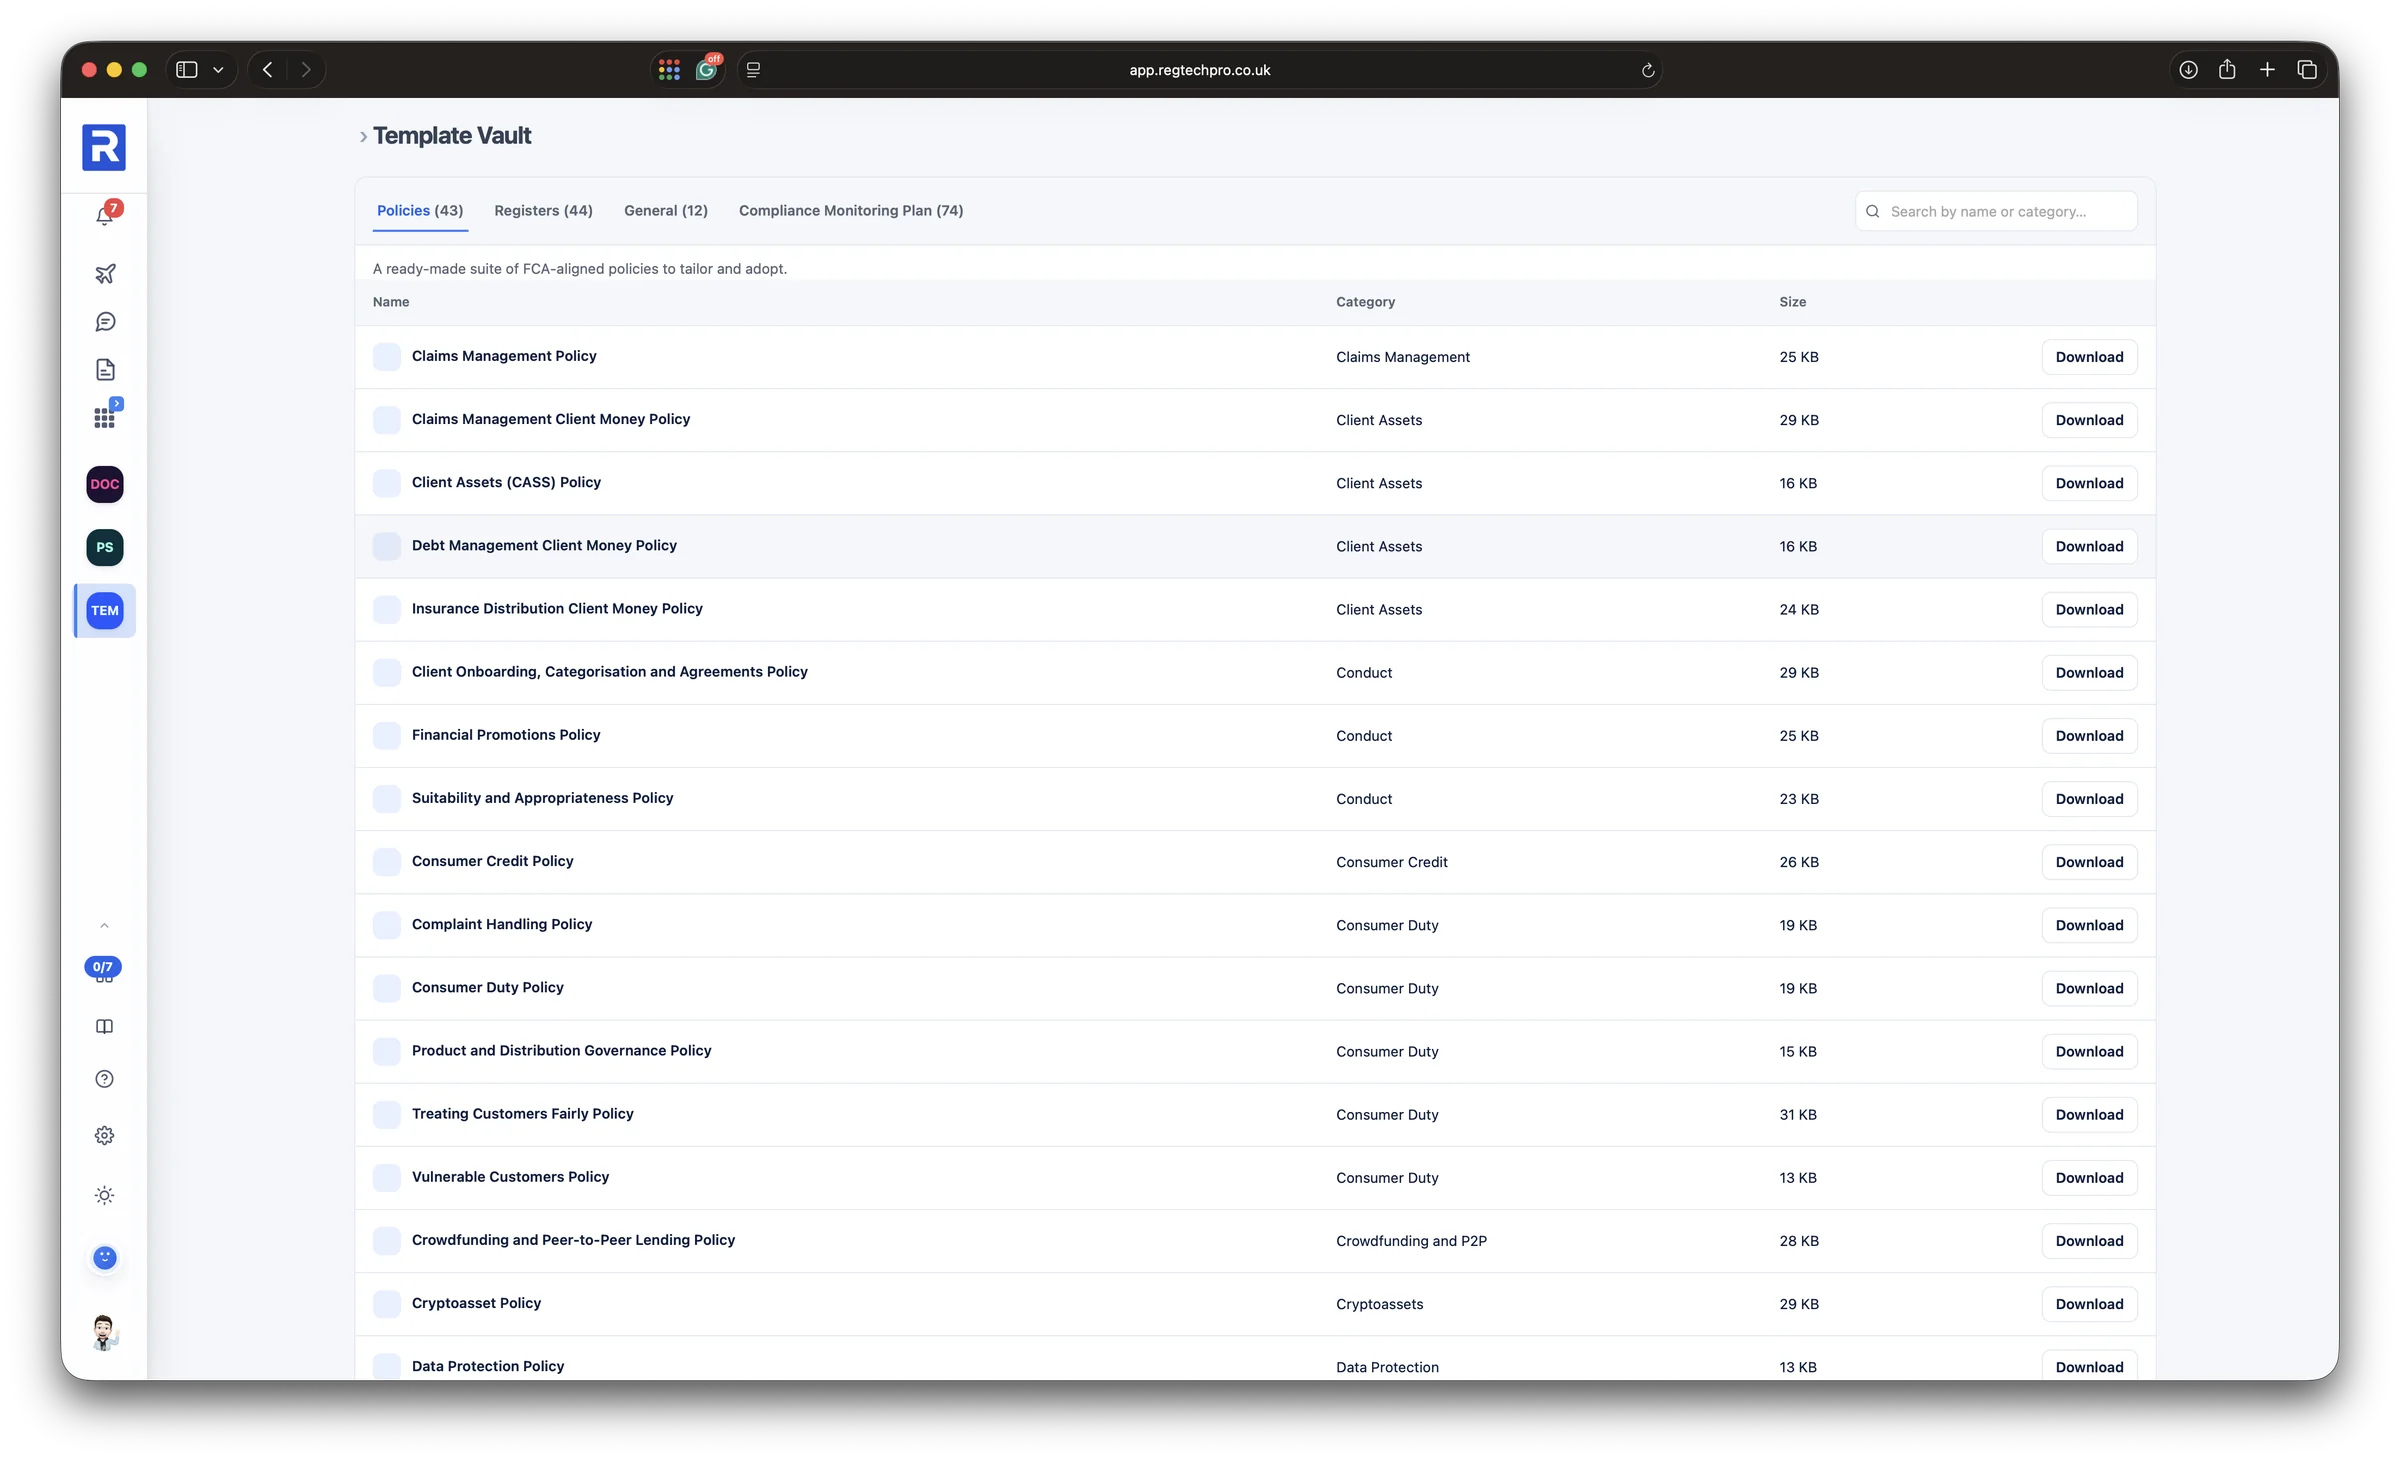
173 ready-to-tailor policies, registers and monitoring-plan chapters
A library of 173 editable Word documents written in-house: 43 FCA-aligned policies across 23 categories, 44 registers designed against the obligation they evidence, 12 standalone forms and notices, and a complete 73-chapter Compliance Monitoring Plan grouped into five parts. Search by name or category, download in one click, tailor it to your firm. No blank page, no per-document consultant fee, no watermarked PDFs.
Who it’s forFirms building or refreshing a compliance framework, firms preparing for authorisation, and consultancies that would otherwise draft the same policy suite for every client.
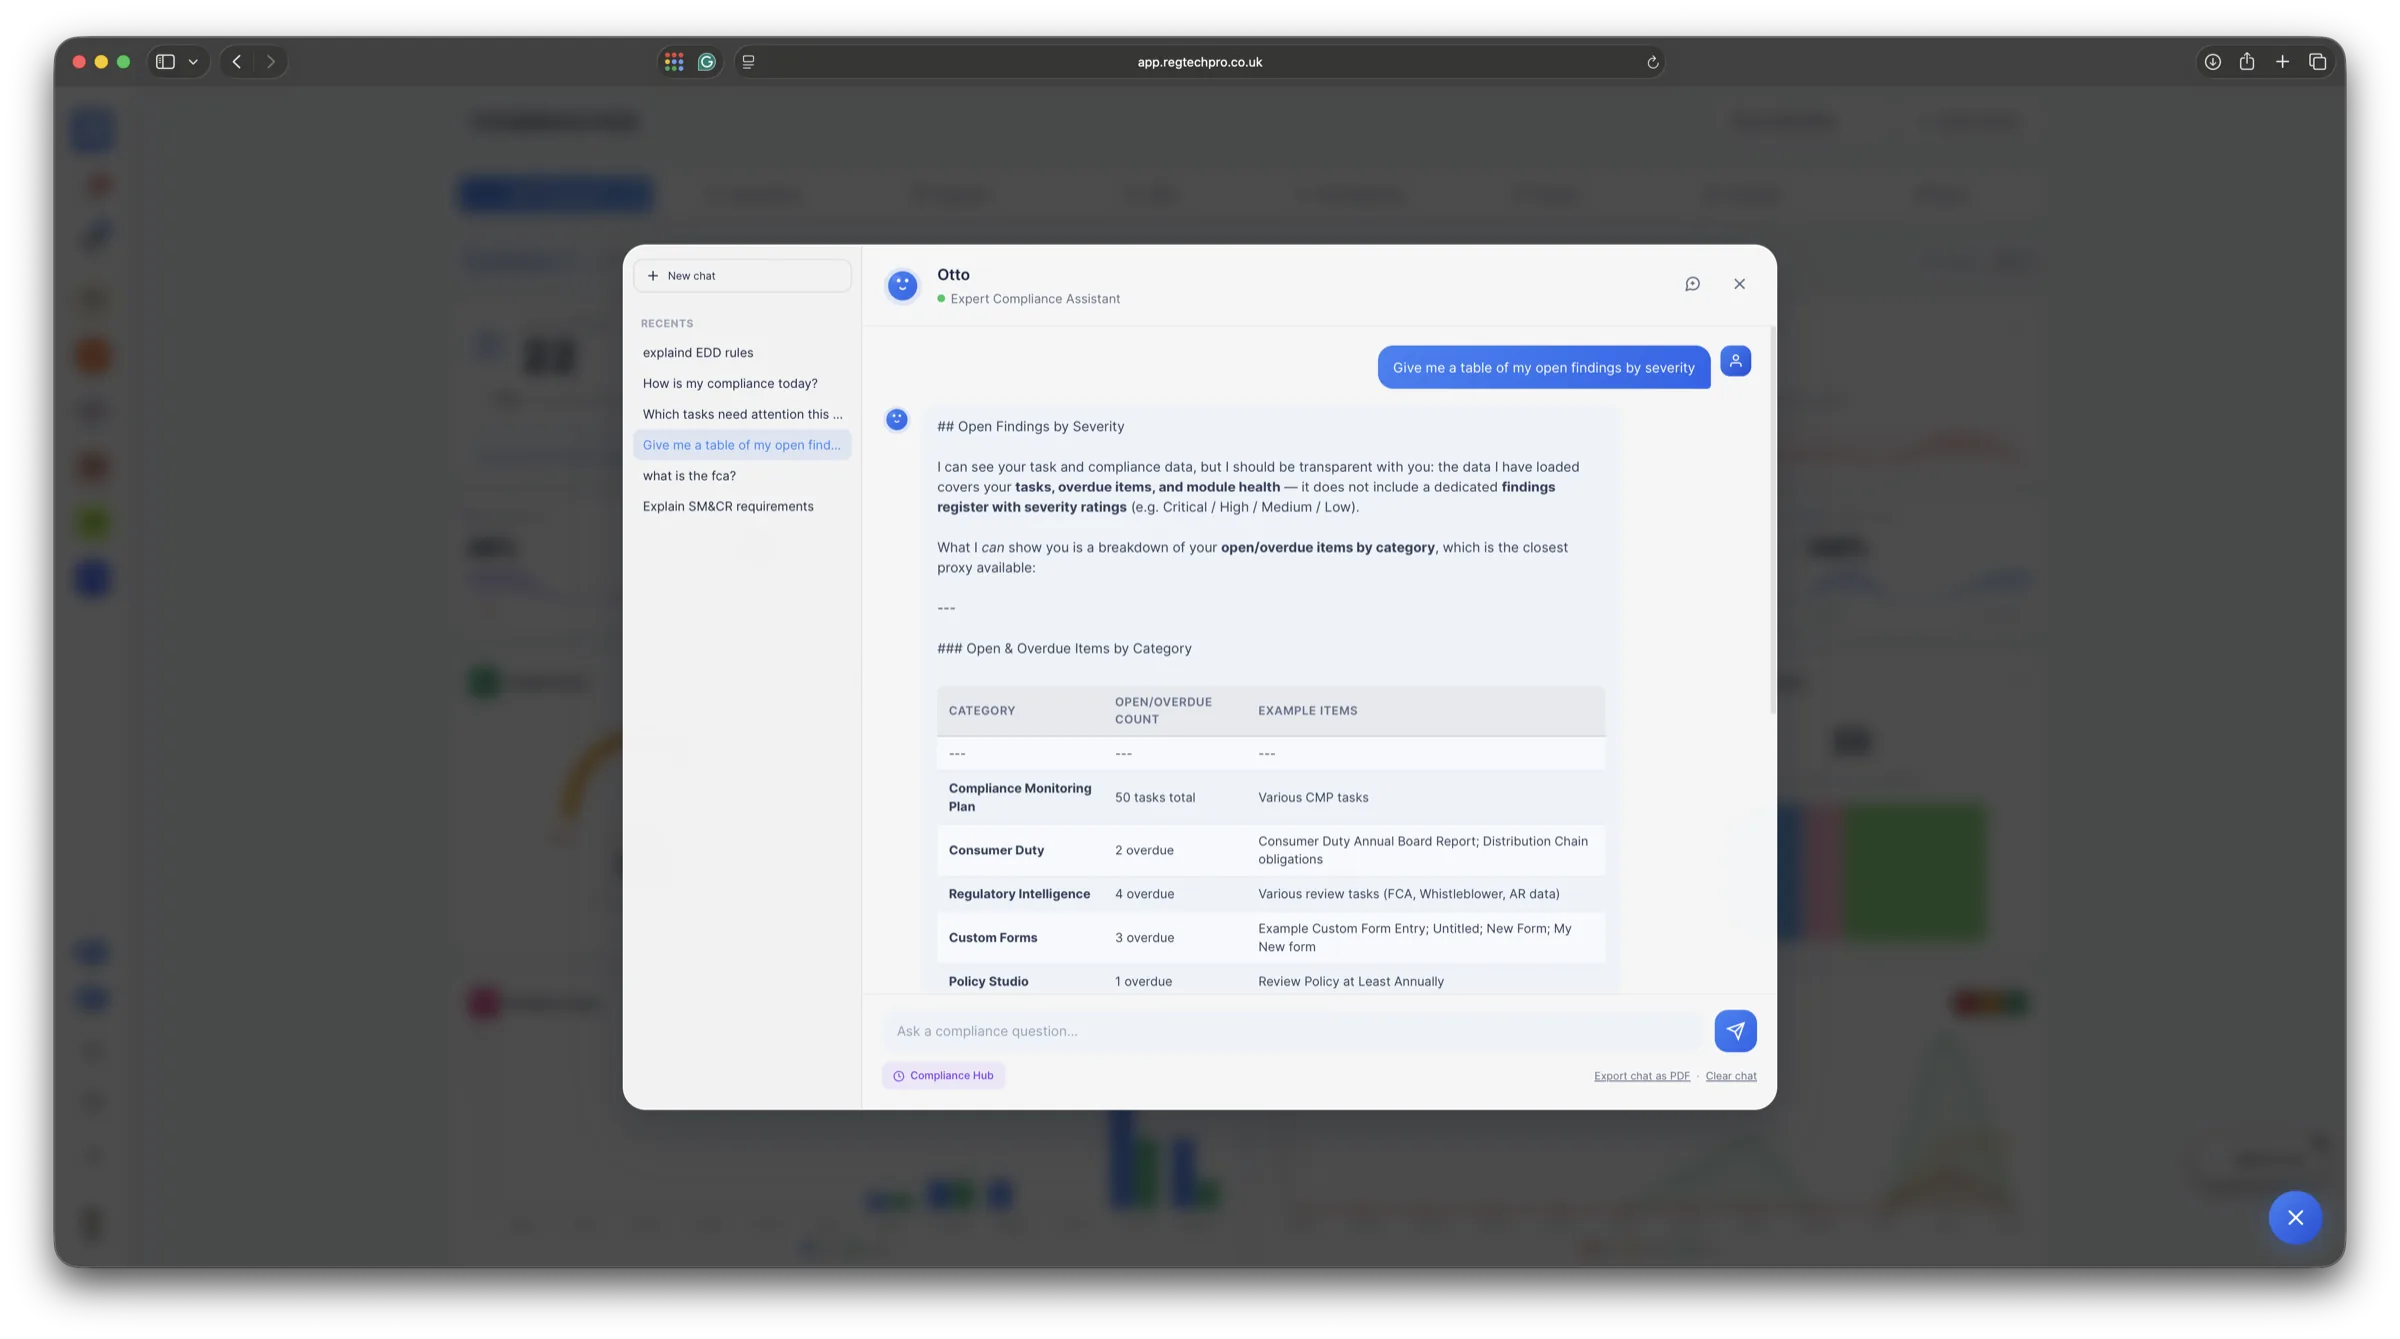
Your compliance analyst, on every page
Otto is the platform’s built-in compliance analyst, and the answer is always drawn from your own records rather than a general summary of the Handbook. Ask what is overdue, where the file is thin or what a rule actually requires, and Otto reads the firm’s live tasks, registers, attestations and findings to answer — naming the module it is reading at the foot of the chat so you can check it. The same engine writes the commentary on every report in Reports: Compliance Monitoring, MLRO annual, DPO annual, Consumer Duty board, Risk Committee and an FCA Readiness mock interview. Otto drafts; a person decides. Nothing is filed, submitted or signed off automatically.
Who it’s forEveryone, on every plan. Otto is included from Starter upwards and behaves the same on every module the firm has switched on.
Three parts of the platform that work across every app, whichever plan you choose.
The rules your permissions bring, read from the FCA Handbook and set beside the checks on your plan that test them.
Your FRN fills in your firm’s details and permissions from the Financial Services Register, and a person’s IRN brings in their roles.
Every ask, answer and attachment kept on the record and linked to the check or record it is about.
Otto is the platform’s built-in compliance analyst — she reads your live data across every module, not a generic handbook summary.
A 12-section Compliance Monitoring Report built from the firm’s live monitoring data, with Otto’s commentary on each section.
MLRO annual, DPO annual, Risk Committee and Consumer Duty board reports in the Reports module, each built from that module’s live records.
The in-platform assistant answers from your own registers, with sources cited — which reviews are overdue, where the file is thin, what closes the gap.
Otto assesses and rewrites a policy, then turns its key commitments into tracked tasks.
AI drafts, humans decide — nothing is auto-submitted.
The short answers before you open a module — or a call.
White-label branding is included with Pro. Add your logo, set your accent colour and sidebar palette, and the platform your team opens every morning looks like it was built in-house — because, as far as they’re concerned, it was.
We use essential cookies to make the site work, and optional analytics cookies to understand how it's used. See our Cookie Policy.